Posts Tagged ‘Open Source’

An End To The Software Industry?

Tuesday, October 13th, 2026

I’ve spent most of my working life as a technical writer, and most of that has been supporting enterprise software of one type or another. For the last couple of years I’ve been on the sidelines because venture capital has flooded into AI to the seeming exclusion of all else, and I have no direct AI experience. Now, thanks to AI, a large part of the software industry may be coming to an end.

First up: Eric S. Raymond:

The end of software secrecy is almost upon us. The death of closed source, and the final triumph of open source.

I should have realized this a few months ago when I successfully decompiled the game of Firefighter from an ancient DOS shareware binary. My robot friend was able to tell it had been written in Borland Pascal from looking at the data layout; it gave me back very readable Pascal code with sensibly chosen function and variable names. I transpiled it to Rust and now ship it as part of my heritage games collection.

The thing is, I thought of this as a fun stunt but didn’t have any confidence that the technique would scale up to large, real programs. I have since learned that people are now doing this sort of thing with entire AAA games, which are among the most complex software artifacts ever to be shipped as a binary. If they can be decompiled, anything can be.

This has implications. Massive implications. We need to think about what the world is like when, in general, there is no longer a secrecy moat around almost any software at all.

I say “almost” because there is going to be one way to maintain secrecy. Software as a service with the executable hiding behind a network connection to the cloud. But as of now, we must assume that anything shipped as an executable, or even a firmware image, is as transparent as glass. It won’t keep its secrets for any longer than it takes for somebody to be motivated to throw an LLM at it.

Snip.

There are still some obstacles. In US law, decompilation of a binary is a derivative work of the binary that falls under whatever copyright it had. However, it is also settled law that if you decompile binary code to a precise specification of what it does, then generate fresh code from that without looking at the decompiled stuff, you’re in the clear. This was the case law that allowed PC clones to exist, after Phoenix Technologies reverse engineered the original IBM PC BIOS.

The two-step process – binary to specification to unencumbered code – will no longer takes a large number of programmers and years of development time. With an LLM, it’s now a thing you can do in a day. Ubiquity will make it impractical to prosecute all the people who might skip the specification step.

Source code can also be covered by patents. You can be able to see their source code for a patented technique and not be able to use it without violating the law. Linux has evolved practices for dealing with this problem – one is not shipping patented video codecs, but requiring you to download them as plugins from jurisdictions where U.S. patents can’t be enforced. This presents patent holders with the impractical challenge of individually suing millions of end users, assuming it can even figure out who they are. To date, AFAIK, this has not been attempted.

I believe Raymond overstates the case a bit, as I bet AIs will find ways to obstuficate executables, but I bet that it will be true in enough cases to drain all the profit out of it for larger software companies that ship executables.

Forced migration from shipped binaries to tied cloud services will be tried – Adobe pioneered this, and Microsoft is pushing it as hard as they can given that their OS is a binary that has to run locally. Both companies are seeing massive user revolts over this. There is good reason to doubt that it’s a strategy that can hold customers in the long term.

However, most software these days doesn’t seem aimed at consumers, it’s aimed at other businesses, the bigger the better. I haven’t seen much if any revolt there. A whole lot of companies seem to have decided they don’t need to own their own software if they can simply have it in “the cloud” and pay a subscription that means they have lower startup costs and can offload the support headcount to a vendor. And it seems that increasingly, that software will be written by AI, tested by AI, probed for security holes by AI, documented by AI, and supported by AI. I wonder if companies will give their AI tech support Indian accents to make them more believable?

But Raymond and other Open Source advocates shouldn’t be so sure that this turn of events is good for their camp as well. Decompilation can just as easily be used to take Open Source executables and create private source clones of them in different programming languages for a variety of different purposes. Also, I suspect that using an AI to add features to Open Source products will be a lot cheaper than hiring an actual Open Source programmer. In fact, I would wager money it’s already being done.

But that’s not the only sign of AI’s threat to the existing software ecosystem. A man has cloned Adobe’s suite and is in the process of doing the same for Microsoft.

Days after unveiling free, open-source stand-ins for seven Adobe applications, Atlanta engineer Brandon Thomas has turned to Microsoft Office. This week he posted WordCraft, GridCraft and DeckCraft – replicas of Word, Excel and PowerPoint – to GitHub, Tom’s Hardware reported. Thomas says he used Anthropic’s Claude to help build the software and is giving the results away.

The Adobe set came first. Gizmodo’s Mike Pearl reported on Oct. 7 that Thomas had used Claude Opus 5.5 and the Rust programming language to recreate Photoshop, Illustrator, Premiere and four other Adobe applications. Thomas wrote on Hacker News that they were in early alpha and “not anywhere close to ready,” while Pearl called the Photoshop stand-in “glitchy, but real.” Adobe, Pearl noted, agreed to a $150 million settlement after federal prosecutors sued it in 2024, alleging it was “trapping” people in subscription plans.

The Office clones followed within days. Paul Thurrott reported on Oct. 9 that WordCraft reads and writes DOCX files, and that ArtCraft, Thomas’s company, calls it 87 percent complete for ribbon commands and about 62 percent complete for real feature parity. For GridCraft, a pre-alpha Excel stand-in, ArtCraft claims 93 percent of Excel’s worksheet functions. DeckCraft, the PowerPoint stand-in, is said to cover about 79 percent of the feature set and to be 80 percent of the way to a first alpha.

Thurrott also reported that ArtCraft has removed the download links from its website, leaving GitHub as the way to get the code.

Gadget Pilipinas took a closer look at the project’s documentation and found some important caveats. WordCraft’s roadmap says charts, SmartArt and embedded OLE objects are lost when a DOCX file is loaded and saved, and validation against real business documents had not yet begun. The site also noted that counting ribbon commands measures whether a feature can be invoked, not whether it actually behaves the way Word does. It listed the licenses as Apache-2.0 or MIT. Release numbers differ between the two outlets: Thurrott reported version 0.3.0, while Gadget Pilipinas cited 0.5.0.

The larger target is the subscription model itself. When Microsoft added Copilot to its consumer plans in January 2025, PCWorld reported, Microsoft 365 Personal rose from about $7 a month to $10 and Family from about $10 to $13, with 60 AI credits a month included. Existing subscribers could remain at the old price on a “Classic” plan.

And the customer base is enormous. Microsoft last reported 89 million consumer Microsoft 365 subscribers in July 2025 and then stopped publishing the metric, according to Office-Watch, which estimates the total is now about 95 million. It also reported that consumer cloud revenue rose 24 percent in the quarter ended June 30.

Even as incomplete products, those efforts should put a chill through the hearts of Adobe and Microsoft executives. Plus, those two companies are among the most abusive in all of tech and richly deserving of their comeuppance, as Louis Rossmann notes.

  • “Adobe is a company that in 2022 said that our automated systems may analyze your content using techniques such as machine learning in order to improve our services and software and the user experience. So, they are using machine learning on your content to improve their system. In 2024, they also pushed out a terms of service update that allowed Adobe’s to have a right to, and I quote, access your content through both automated and manual methods. When Adobe did that, they did not give you any ability to opt out of this. There was no opt out button present anywhere. And if you wanted to get access to your session files again for the things that you were paying Adobe to be able to work on, your private files, you had to accept this update to the terms of service.”
  • ” I think most of my audience, even the anti-AI people can agree that when a company routinely and repeatedly fucks over its customers for decades by turning software that you own into a subscription, by charging gigantic cancellation fees that are not very obvious, by trying to get access to your fucking content and not allowing you to say no to it, by increasing the price every single year, by not allowing you to activate the software that you’ve already bought and paid for, that when somebody comes along and uses AI to poop out a clone that does 99% of it for free. That’s pretty cool. I’m on AI’s side there.”
  • He covers more on the theoretical legalities of the move in relation to the DMCA and other federal law, so watch the whole thing if you’re interested in the details.
  • This is all great for people who hate Adobe’s and Microsoft’s user-hostile and anti-competitive practices, but the capabilities are fairly ominous for the software industry as a whole. It used to take a year or more for a dedicated programming team to churn out even a basic clone of a popular software product. Now one guy with sufficient AI tokens can do it in less than a week. (And don’t get me started on the whole “token economy” BS, which is an entirely different rant.) Given that, the desire to fund new software startups is going to be deeply disincentivized.

    It’s ironic how the one thing AI has proven good at is replacing the jobs of the software engineers that helped create it.

    Before the 1980s, hardware was king in tech. Chips and computers were expensive, and software was merely a way to sell more hardware. Then a variety of software companies (Lotus, Microsoft, Adobe, Boreland, Ashton-Tate, Intuit, etc.) managed to build business empires worth many multiples of their higher cost software brethren, a trend that only accelerated with the arrival of the World Wide Web. (Apple is a special case, in that their software still exists to drive hardware sales.) Now, thanks to the AI boom/bubble, it’s hardware and AI companies generating the huge valuations, with software profits under threat.
    Just as in previous tech revolutions, I’m sure someone will figure out how to build business empires on the top of AI tools, but just like the Internet circa 1988, no one has figured out just how yet…
    LinkSwarm for May 5, 2023

    Friday, May 5th, 2023

    A Soros-backed DA is stepping down, a Harvard prof lying about playing footsie with commies sentenced, and another Democratic fundraiser convicted of fraud. It’s the Friday LinkSwarm!

  • Good news, everyone! Soros-backed St. Louis Democrat DA Kim Gardner has resigned.

    On Thursday, a progressive prosecutor who was notoriously funded by far-left billionaire George Soros announced her resignation, after months of bipartisan pressure to do so.

    Fox News reports that Kim Gardner, the Circuit Attorney for St. Louis, announced that her resignation will be effective June 1st. Gardner was one of the first prosecutors in the country to be bankrolled by Soros, who has since expanded his efforts to other major cities across the country. She was first elected in 2016 and re-elected in 2020, largely due to Soros’ financial backing. Prior to her resignation announcement, she had declared her intention to run for a third term in 2024.

    After years of criticism for being soft on crime and siding with criminals over victims, Gardner faced a whole new wave of criticism from both parties over an incident in February: Teenage volleyball player Janae Edmonson, who was visiting St. Louis from Tennessee for a tournament, was hit by an out-of-control car while crossing the road; although Edmonson survived, she had to have both of her legs amputated.

    The driver of the car was Daniel Riley, a man who was out on bond while awaiting trial for an armed robbery case. It was later revealed that Riley had violated the terms of bond dozens of times, but was never arrested. When the blame turned to Gardner for failing to keep him off the streets, she falsely claimed that her office had attempted to have Riley jailed once again, only to be denied by a judge; there are no records of her office filing any such motion or otherwise seeking the revocation of Riley’s bond.

    Following the Edmonson incident, Missouri Attorney General Andrew Bailey (R-Mo.) filed a petition quo warranto, the process by which the state attorney general can fire a prosecutor who has been determined to be neglectful of her duties. Bailey claimed that as many as 12,000 criminal cases have been dismissed due to Gardner’s failures, with another 9,000 having been thrown out right before they were set to go to trial, due to Garnder’s office refusing to provide evidence and speedy trials for defendants.

    After Gardner’s announcement, Bailey released a statement demanding that she vacate her office immediately, rather than wait for another month.

  • The Biden Banking Crisis continues to bubble along. First Horizon, PacWest, and Western Alliance are the new banks facing trouble. (Hat tip: Stephen Green at Instapundit.)
  • “Wagner Chief to Pull Mercenaries Out of Bakhmut over Ammunition Dispute with Russian Military.”

    Wagner Group chief Yevgeny Prigozhin said he will pull his mercenaries out of the meat grinder that is the Ukrainian city of Bakhmut on May 10, one day after Russia’s Victory Day Celebrations, which Russian president Vladimir Putin is expected to use to shore up support for the Russian invasion.

    The Wagner Group, a well-known mercenary unit known to be one of Russia’s most competent fighting divisions, is leading the charge on Bakhmut, a city that that has gained outsized symbolic importance.

    “I am withdrawing the Wagner PMC units from Bakhmut, because in the absence of ammunition they are doomed to senseless death,” Prigozhin said in full military fatigues and carrying an automatic weapon. The video he released showed him surrounded by masked Wagner fighters. Prigozhin also released a statement to the same effect.

    His forces had no choice but to withdraw to rear bases to “lick the wounds,” said Prigozhin, as translated by the Washington Post. If Wagner goes through with the withdrawal, it would be viewed as catastrophic in terms of morale. The Russian invasion has ground to a standstill after large-scale Russian and Ukrainian offensives last year. Kyiv, which has been amassing ammunitions including tanks and fighter jets, is expected to launch a fresh counterattack in the very near future.

    Prigozhin also launched a remarkable video tirade overnight on Telegram in which he displayed bodies of dozens of Wagner soldiers killed in Bakhmut. He angrily laid into the Russian Defense minister Sergei Shoigu and Valery Gerasimov, chief of the general staff of the Russian armed forces, for supplying Wagner with only 30 percent of the ammunition that’s needed.

    The statement released today claimed that number was even lower, standing at 10 percent.

    One caveat is that we’ve heard complaints from Prigozhin about his ammo supply before.

  • Russian soldiers dig trenches in horse graveyard in occupied Ukraine. Now they have anthrax.
  • “Biden CIA chief met with Epstein several times after financier convicted of child sex crime. Central Intelligence Agency Director William Burns had three meetings with Jeffrey Epstein in 2014, when the top spy official was deputy secretary of state and after Epstein was convicted of child sex exploitation.” (Hat tip: Stephen Green at Instapundit.)
    

  • “Harvard chemistry professor sentenced for lying about ties to CCP…Former Harvard University Chemistry Department Chair Charles M. Lieber was sentenced Wednesday to time served and over $80,000 in fines for committing fraud and for failing to disclose his connections to the Chinese Communist Party.” (Hat tip: Instapundit.)
  • “Longtime Democratic Campaign Strategist Charged with Election Fraud.” And completely different than the Democratic Party fundraiser convicted of fraud last week.

    New Jersey Democratic campaign strategist James Devine was charged with election fraud for allegedly submitting more than 1,900 fake petitions to help secure a 2021 Democratic gubernatorial primary ballot spot for candidate Lisa McCormick, New Jersey Attorney General Matthew Platkin announced Tuesday.

    Devine was McCormick’s campaign manager and sent the fake voter certifications to the New Jersey Secretary of State’s Division of Elections via email in April 2021, but the New Jersey Democratic State Committee challenged his attempt days later, arguing that all the forms featured same the style of signature and at least one of the named voters was deceased, Platkin said.

    A judge subsequently took McCormick off the primary ballot, and Devine is now charged with third-degree offenses concerning nomination certificates or petitions, tampering with public records or information and fourth-degree falsifying or tampering with records.

    (Hat tip: Instapundit.)

  • “Kansas Becomes 1st State to Pass Law Defining Gender as a Person’s Sex at Birth.” One down, forty-nine to go…
  • Killer in Satan’s service finds the left’s child sexual mutilation fetish disgusting.
  • Shots of Minneapolis before and after the Antifa/BLM riots of 2020.
  • “El Paso Engulfed In ‘Mass Migration Dumpster Fire‘ As State Of Emergency Declared.”
  • Accused serial black widow killer charged with murdering her fifth husband.
  • “You just killed two people tonight.” “Yeah, but when can I go back to school?”
  • California banning diesel effective 2036.
  • Could sexbots and AI end humanity?
  • “Googlers angry about CEO’s $226M pay after cuts in perks and 12,000 layoffs.” Funny how you never hear the “Occupy Wall Street” crowd going after the Sundar Pichais of the world.
  • Speaking of Google, I’m hardly an expert on AI, but here’s a piece that claims Google is getting its clocked cleaned by OpenSource AI.

    LoRA updates are very cheap to produce (~$100) for the most popular model sizes. This means that almost anyone with an idea can generate one and distribute it. Training times under a day are the norm. At that pace, it doesn’t take long before the cumulative effect of all of these fine-tunings overcomes starting off at a size disadvantage. Indeed, in terms of engineer-hours, the pace of improvement from these models vastly outstrips what we can do with our largest variants, and the best are already largely indistinguishable from ChatGPT. Focusing on maintaining some of the largest models on the planet actually puts us at a disadvantage.

    (Hat tip: Ace of Spades HQ.)

  • The Case of the Disappearing Swiss Cheese Holes.
  • Wes Anderson’s Star Wars.
  • A nice stroke of book collecting luck: I picked up an inscribed presentation copy of H. G. Wells’ The Food of the Gods. Or rather, I picked it up as part of a multibook lot back in February and didn’t realize it was inscribed until last week.
  • “Biden Deploys 1,500 Troops At Border To Help Register New Voters.”
  • “Pro Disc Golfer Disqualified After Testing Negative For Cannabis.”
  • Log4J and Internet Castles Made of Sand

    Thursday, December 16th, 2021

    If you work outside of a tech company, chances are you’ve spent this week primarily concerned with getting ready for Christmas. If you work inside a tech company, there’s a significant chance your company spent much of this week patching a critical vulnerability in an open source Java logging library called Log4J.

    Here’s a non-technical explanation of the problem:

    It’s a vulnerability that was discovered in a piece of free, open source software called log4j. This software is used by thousands of websites and applications, to perform mundane functions most people don’t think about, such as logging information for use by that website’s developers, for debugging and other purposes.

    Every web application needs functionality like this, and as a result, the use of log4j is ubiquitous worldwide. Unfortunately, it turns out log4j has a previously undiscovered security vulnerability where data sent to it through that website — if it contains a special sequence of characters — results in log4j automatically fetching additional software from an external website and running it. If a cyberattacker exploits this, they can make the server that is running log4j run any software they want — including software that can completely take over that server. This is known as a Remote Code Execution (RCE) attack.

    To use a technical phrase, this is Really Bad.

    The net result is that, left unaddressed, cyberattackers right now can completely take over thousands of websites and online applications, allowing them to steal money, data, and access. The security community has been completely focused on this vulnerability for the past two days, and updating servers running log4j as quickly as possible to protect against this vulnerability.

    The good news is that mitigations are relatively easy to implement. The bad news is that left unmitigated, the vulnerability is extremely easy to exploit. iCloud, Minecraft, Baidu, and many other sites have been confirmed to be vulnerable so far, and you’ll likely hear more about many other sites being vulnerable in the coming days.

    And those companies are just the tip of the iceberg. LAMP stacks (Linux, Apache, MySQL, and PHP) are used as the technological underpinnings for a wide variety of web applications of all sizes. (It’s not universal, as NGINX has taken over as a market leader from Apache, and there are still a few all-Microsoft houses that use IIS, and neither of them have the vulnerability.)

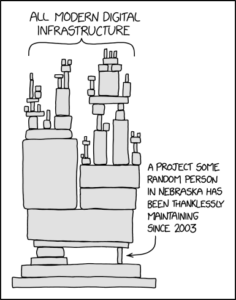
    Open Source has been a revolutionary invention because it provides rapid development by armies of distributed developers, and Linus’s Law states that “with enough eyes, all bugs are shallow.” But there are tens of thousands of Open Source components out there running critical infrastructure that haven’t had nearly as many eyes on the code as the Linux kernel. It’s simply the nature of the beast. XKCD had a cartoon for this occasion:

    Internet applications gain usefulness from widespread adoption and the number of other components they tie into and support. You know what creates new vulnerabilities? A larger user base and the number of other components they tie into and support, which creates more attack surfaces for malicious actors to exploit.

    The flaw isn’t the fault of Random Guy in Nebraska, the fault is the company adopting software that they can’t possibly test for all the use-cases they’re going to use it for. Surprise! Just about every high tech company in the world is in the same boat. Pretty much everyone uses a wide panoply of open source tools for their Internet applications, and no one can test all the permutations of how each component might be put to use.

    You can’t eliminate the risk, you can only minimize and mitigate it. You can use containerization strategies (Docker, Kubernetes, Container D, etc.) to minimize attack surfaces and limit contagion. You can run all your code through security scanning tools on your CI/CD platform of choice. You can do constant testing and keep rolling backups of everything to limit risk and speed recovery. (You can also train your employees not to click on random email links without verifying the sender is who they say they are, and not to give any any account information or passwords over the phone, and train them enough so that the lessons stick, even though phising and human engineering weren’t factors in the Log4J vulnerability.)

    But there still a good chance that the platform you’re using today is different than the platform you’ll be using ten years from now, and you’ll have to go through the same learning lessons discovering new vulnerabilities for the new platform all over again.

    Castles made of sand all fall into the sea eventually…