The 25th Anniversary of the 9/11 attacks, GOP midterm convention, Iran and Yemen both get spicy again, AfD shocks Germany, Ukraine’s longest drone strike yet, more welfare state fraud, more money for Paxton,
It’s the Friday LinkSwarm!
More information about the murder of my friend Andrew Wimsatt has come out, and some of my original post needs to be corrected. I’m going to put that in a Saturday post, and there will be another for remembering Andrew on Sunday.
On a perfectly clear morning 25 years ago, America changed forever.
At 8:46 a.m. on that day, a team of Islamic terrorists crashed American Airlines Flight 11, carrying 76 passengers and eleven crew members, into the North Tower of the World Trade Center. It was followed 17 minutes later by United Airlines Flight 175, carrying 51 passengers and nine crew members, which terrorists steered into the South Tower. Less than 90 minutes later, both of those towers had collapsed into a massive pile of rubble.
Meanwhile, as Americans’ televisions were tuned to live footage of the burning buildings, American Airlines Flight 77, carrying 53 passengers and six crew members, was slammed into the Pentagon. And shortly after, United Airlines Flight 93, with 33 passengers and seven crew members, crashed in a field in Shanksville, Pa.
Today, we remember the 2,977 innocent victims who were the first casualties in what would become known as the War on Terror. We also remember the extraordinary heroism displayed that day, without which the horrific losses would have been far worse.
One of the most miraculous facts about that day was that at the World Trade Center, which may have had an occupancy of 19,000 people between the two buildings at the time, 99 percent of those who were below the point of impact of the planes survived. This achievement is owed to the extraordinary evacuation efforts of first responders, who ran into burning buildings, no doubt knowing that there was a good chance they wouldn’t make it out. In the end, 441 firefighters, police officers, and paramedics did not.
Then there was the civilian heroism displayed by the passengers on Flight 93, who had heard about what happened at the World Trade Center, overtook the plane, and ensured that it crashed in an empty field rather than into the U.S. Capitol or White House, one of which was believed to be the potential target. Passenger Todd Beamer’s remark to his fellow passengers, “Let’s roll,” overheard from a phone call, became a rallying cry as the nation fought back.
I have no dramatic, notable 9/11 stories to tell. I was driving to my job at Applied Materials when NPR (yes, I sometimes listened to them in the morning, back in the day) broke into regular coverage to report the first tower impact. I heard a rumor that the layoff that came next week (as the depths of the Dotcom Bust were just being felt) was actually scheduled for that day, but they decided to hold off due to the attacks. Ironically, one of the people in one of the planes was an Israeli Applied employee, who survived a country beset by terrorism only to be killed on an American flight.
President Donald Trump delivered the convention’s closing remarks following a keynote address from Vice President J.D. Vance.Before they took the stage, though, Texas Republicans used their appearances to focus on the November elections, public safety, immigration, and the direction of the Democrat Party.
Lt. Gov. Dan Patrick invoked Texas history and the Alamo before turning to the November election, portraying the contest as a broader fight over the country’s values.
“This election coming up is not about politics,” said Patrick. “It’s about darkness, and it’s about light.”
He accused Democrats of embracing socialism and communism and argued that Texas’ economic growth has been driven by conservative policies including low taxes and no state income tax.
He also singled out Democrat Senate nominee James Talarico, saying Republicans would put “the Democratic Party and James Talarico and his ilk on the dust heap of history.”
Patrick closed his remarks by urging Republicans to view the election as a fight for their families and the country. “You started a fight, and the Republicans are going to finish it in November.”
Eric Flores and Tano Tijerina, two Republican candidates challenging Democrats in South Texas, also addressed the convention. Their appearances highlighted Republicans’ continued focus on South Texas, where the president made significant gains in 2024.
U.S. Sen. Ted Cruz used his speech to warn about what he described as an emerging red-green alliance between communists and Islamists. He received one of the strongest reactions from the crowd when he declared that Sharia law is incompatible with the U.S. Constitution.
“Sharia law has no place in America,” said Cruz. “Sharia law is fundamentally inconsistent with the Constitution, and we need to stand together and stop it now.”
Gov. Greg Abbott focused much of his speech on Texas Democrats running statewide in November, contrasting their legislative records with policies he has signed into law.
Abbott pointed to the GOP’s success on a variety of issues including border security, policing, property taxes, oil and gas, election laws, parental rights, and school choice.
“All the Democrats running statewide in the state of Texas, they had a chance to vote on those policies, and they voted against those policies,” said Abbott. “They voted against common sense.”
Abbott highlighted legislation he signed prohibiting cities that reduce police funding from receiving certain state tax revenue, restricting some purchases of Texas property by citizens and entities tied to China, Russia, Iran, and North Korea, and prohibiting gender mutilation procedures for minors.
Snip.
Vice President J.D. Vance delivered the night’s keynote address, reflecting on the administration’s first 19 months back in office and making the case for Republicans in November.
Vance also paid tribute to Charlie Kirk on the anniversary of his assassination, recalling that Kirk had been in the front row when Vance addressed the Republican National Convention as the party’s vice presidential nominee in 2024.
Turning to Texas politics, Vance took aim at Democrat U.S. Senate nominee James Talarico over his previous comments on gender and Christianity.
“This Talarico guy—he will not shut up about how there are six genders. He will not shut up about how, ‘God is non-binary,’” said Vance.
“I gotta say, a guy that age who is so obsessed and focused on transgender children-I don’t know about you, but I never want to see that guy’s web browser.”
Last night Germany’s much-maligned AfD party won a crushing and historic victory. The victory is already being downplayed by many, owing to the fact that Saxony-Anhalt is technically one of Germany’s smallest and least consequential states. But there is far more to it than sheer numbers, as the win defines a turning point not only in German but European politics, and cements the gradual downfall of the globalist ruling class that has tried desperately for decades to keep populist movements from gaining power, in particular utilizing the “Brandmauer” or “firewall” to suppress the so-called far-right.
The destruction of this firewall is an historic occasion, even if it should come by way of such a seemingly inconsequential state.
Of course, there are other criticisms as well. AfD is seen by many as a kind of Trojan horse, a German “MAGA” party led by a lesbian woman in Alice Weidel. Even so, it represents a striking loss of power for the elites and a turning point which breaks a kind of psychological barrier that will only energize other anti-establishment, “far-right”, or populist parties throughout Europe.
Another secondary effect of the victory is that it has caused the ruling German establishment to go back to the drawing board and review its most unpopular policies, like on immigration, in order to bend with the clearly changing winds.
Merz expressed his “deep shock” at the election result, foreseeing it having major repercussions on Germany as a whole:
The AfD, however, fell just three seats short of an ‘absolute majority’ which would have allowed it to govern the state alone. Some commentators have pointed out some major ‘anomalies’ in regard to mail-in versus in-person votes. Just like in the highly irregular American 2020 election, every party but AfD was allegedly boosted by disproportionate numbers of mail-in votes:
More analysis at the link. Just think if Germany’s elites hadn’t decided to import millions of unassimilated Muslims into their country, they wouldn’t have empowered the AfD. (Hat tip: Director Blue.)
Yemen has also been getting spicy, with the Iranian-backed Houthis driving for the coast, successfully attacking a Saudi pipeline, and the official anti-Houthi government of Yemen making gains in the interior. More from Preston Stewart. If this week hadn’t been so insane, I might have done a separate post on this…
Maybe this is why I’m still unemployed. “Women Filled 98 Percent of Jobs Created in August.”
Women accounted for 158,000, or 98 percent, of the 162,000 nonfarm payroll jobs created in August, according to the Bureau of Labor Statistics’ establishment data. Compared to this time last year, there are 870,000 more women employed in the U.S., according to the Bureau of Labor Statistics, and 1.5 million fewer employed men.
So there were only 4,000 men hired in August.
Accounting for the new data, the gap between male and female employment reached its highest level since 1990, when men were overrepresented in the workforce.
Dramatic month-to-month swings in employment gains between the sexes are relatively common, and labor economists warn that sharp shifts don’t necessarily indicate lasting changes in the market. However, the August jobs report is in keeping with existing trends that have obtained for decades, namely a substantial increase in employment among women and a linear decline in employment among men.
There has been a “multi-decade decline in male labor force participation” and a “multi-decade increase in female labor force participation,” Kirk Doran, a professor specializing in labor economics at Notre Dame University, told National Review.
Part of this shift can be explained by the evolution of American industries. The sectors that grew at the highest rate in August — health care and public education — are female-dominated. Meanwhile, the industries that shrank — computing, data processing, and finance — are male-heavy.
We have every reason to be excited to go to the polls to ensure an ongoing Congressional Republican majority, and to keep the DSA-influenced Democrats away from any levers of power.
The 20 months since President Trump’s inauguration in early 2025 have had the most significant conservative victories of my lifetime, far exceeding President Reagan’s accomplishments. Here are just a few of the things President Trump and his team have done:
Closed the border to illegal invaders.
Deported hundreds of thousands of illegal aliens, and caused millions more to self-deport.
Slashed the federal workforce.
Eliminated DEI and wokeness from the military and federal agencies.
Eliminated EV mandates and green energy subsidies.
Effectively terminated corporate average fuel economy requirements for auto manufacturers.
Engaged the military to eliminate narco-terrorists.
Engaged the DOJ to target corporations engaged in illegal racial discrimination in hiring.
There are so many more milestone accomplishments beyond those.
For decades the conservative base has clamored for the above victories. President Trump finally delivered. Amidst all this, there are many “conservative” influencers who are promoting doom. For many of them, that is their job – being paid to blackpill conservative voters to stay home, so as to elect a Democrat Congress. The resumption of Democrat lawfare against the Trump administration is their goal.
Despite razor-thin congressional majorities, Trump47 has delivered numerous policy wins, and conservatives (and anyone else who wants to stop the insane, jihad-friendly, socialism- and social justice-infected Democrats from reclaiming power) should head to the polls in November to ensure Republican control through 2028.
“Ukraine’s Longest Range Drone Strike Yet! Nearly 3,000km! Plus Strikes on Sochi and Dagestan.” “Ukrainian drones carried out their longest range drone strike to date, hitting Russia’s Novy Urengoy and Purovsky gas processing plants in Yamalo-Nenets.” Yamalo-Nenets is an “autonomous okrug” on the Arctic Circle just east of the Urals.
Quality Care Access, LLC was chartered in July 2020 by Jovin Bayingana, and the Portland-based company rapidly became one of the most lucrative new MaineCare businesses in New England.
According to Medicaid payment records obtained via a Freedom of Access Act request, the company billed the Department of Health and Human Services (DHHS) for $1.2 million in 2021, $5.3 million in 2022, $7.4 million in 2023, $6.7 million in 2024, and $7.2 million in 2025 — for a lifetime cost of $27.8 million.
The more detailed federal Medicaid dataset shows that throughout this time frame QCA had fewer than 16 patients in most years.
Finally: “Republican Reinforcements Arrive for Paxton in Senate Race. The Senate Leadership Fund is pouring millions into Texas after questions over whether the Cornyn-aligned group would back Paxton.”
Republican reinforcements are finally arriving for Attorney General Ken Paxton in his U.S. Senate race, months after the party’s biggest Senate-focused outside group backed his primary opponent.
The Senate Leadership Fund, a super PAC aligned with Senate Majority Leader John Thune, has purchased $32 million in television advertisements across Texas and is reportedly preparing to spend more than $50 million to support Paxton against Democrat James Talarico.
The group announced Friday it created a new Texas PAC dedicated to the race, with ads promoting Paxton and contrasting his record with Talarico expected to run continuously through Election Day.
The investment ends months of uncertainty over whether the Senate Leadership Fund would support Paxton after backing Sen. John Cornyn in the Republican primary.
It also comes as other major Republican groups have already begun pouring money into the race.
MAGA Inc., the super PAC aligned with President Donald Trump, recently announced $10 million in advertising supporting Paxton. America PAC, the political group backed by Elon Musk, is also supporting Paxton and has begun door-knocking operations to register and get out the vote.
This is good, if overdue news, but media ad spends are the fools gold of politics. The same group spending zillions for Cornyn didn’t move the needle, so the efficacy of their political efforts seems debatable. But maybe they’re better at convincing squishy moderates than Republican primary voters…
Democrat Texas House candidate Oziel Ochoa’s campaign sponsored a May Day event co-hosted by the Rio Grande Valley chapter of the Democratic Socialists of America.
Ochoa is challenging Republican State Rep. Janie Lopez for House District 37, a South Texas district covering Willacy County and portions of Cameron County.
Campaign finance records show Ochoa’s campaign made three $259 payments to La Union del Pueblo Entero, or LUPE, on May 4. The expenditures, totaling $777, were listed as advertising expenses for the first annual May Day Marcha del Pueblo (March of the People).
May Day, also known as International Workers’ Day, is an annual labor observance that has long been embraced by socialist and communist movements around the world.
The event took place two days earlier, on May 2, in Edinburg.
Organizers included LUPE, Texas Rising, the Rio Grande Valley American Federation of Teachers, the Rio Grande Valley Central Labor Council, South Texans for Reproductive Justice, Poder Latinx, and the Rio Grande Valley Democratic Socialists of America.
Ochoa was publicly recognized for his financial support, while RGV DSA was listed among the event’s organizers.
The former police chief of Hamtramck, Michigan, is in hot water after investigators have dug into allegations against the Muslim chief for how he ran his department.
Court records show that Hamtramck Police Chief Jamiel Altaheri personally engaged in a “pattern” of domestic violence in his own household, and told officers that wife-beating isn’t a “formal” crime.
The primary effects of Democrats importing unassimilated Muslims for political advantage seems to be more wife-beating and more rape.
“Criminal Illegal Alien Arrested in Texas, Ordered Deported 26 Years Ago. A Cuban national who evaded deportation for 26 years is now behind bars.” “According to ICE, Cuban national Emiliano Martinez Perez entered the United States around 1998 and was convicted of cocaine possession shortly afterward. He was ordered to leave the U.S. in early 2000, but remained in the country and was later convicted of drug trafficking in 2007.”
Speaking of immigration fraud: “Houston Immigration Attorney Arrested for Fraud. Nowowiejski allegedly committed mail fraud and made false statements related to immigration cases.”
A Houston immigration attorney was arrested Wednesday after a federal grand jury indicted her on charges of mail fraud and making false statements related to her work on behalf of immigrants seeking work-related legal status in the United States.
Alla Nowowiejski is a naturalized citizen from Russia and has practiced law in Texas since 2009 and specialized in business immigration assistance, but she allegedly never submitted, or only partially submitted, paperwork for clients seeking to obtain work status or work visas.
The indictment also alleges that Nowowiejski provided clients with false documents or reference numbers tied to active immigration cases unrelated to her own clients to make them believe their applications were being processed.
In 2023, Audubon Engineering Operations sued Nowowiejski for gross negligence and legal malpractice in Harris County. The company alleged that although she had charged them more than $109,000 for immigration work on behalf of five employees, she never filed paperwork with federal immigration agencies.
“Chaos ensues in Democratic Party after Arab reporter calls black congressman ‘AIPAC monkey.'” Arab reporter is Rula Jebreal (who, I guess, is most famous for dating Roger Waters) and the black congressman is Hakeem Jeffries. Hakeem Jeffries should never be called a monkey, only “TEMU Obama.”
The deal would mark the first chunk of change the nation will provide to the U.S. under South Korea’s new $350 billion commitment.
Last year, tariff talks between the U.S. and South Korea led to a 10 percent decrease in tariffs imposed on South Korea — a drop from 25 to 15 percent — provided the country invests $350 billion in the U.S. in exchange.
The power project would be set in Encinal, Texas, a small city in La Salle County.
According to The Korea Herald, talks initially began with South Korea proposing $19.8 billion for the project, and the U.S. countering with $25 billion. Negotiations will now proceed in the $22.6 billion range, although the exact amount will not be determined until the project is finalized.
The proposed gas combined-cycle project plant would total 6.3 gigawatts (GW) of power, built in stages. The first stage will consist of a 1.4-GW gas turbine power facility. Once the first stage passes inspection, the second stage, a 4.9-GW combined-cycle facility, will be built.
Though unconfirmed, the plant is expected to help meet the state’s booming demands for artificial intelligence (AI) computing capacity, data center development, and semiconductor development.
Microsoft Corp. today issued updates to plug at least 974 security holes in its Windows operating systems and other software, by far its biggest single patch batch ever. Microsoft says artificial intelligence is helping to speed the discovery of vulnerabilities, but security experts warn that many organizations already are struggling to prioritize the more human-intensive endeavor of testing and deploying so many fixes each month.
This month’s patch bundle obliterates the software giant’s previous record set in July, when it released updates for at least 570 security vulnerabilities. September’s Patch Tuesday brings this year’s total to more than 2,600, more than twice Microsoft’s previous record-setting patch year in 2020 (1,245) and with three more months to go.
There are two “zero-day” flaws fixed this month that are being actively exploited: both CVE-2026-81963 and CVE-2026-85880 allow an attacker to elevate their privileges on Windows system.
Fully 113 of the bugs addressed today earned Microsoft’s “critical” rating, meaning they could be abused by malware or miscreants to seize control over a vulnerable Windows machine with little or no help from the user.
Among the more serious critical flaws this month is CVE-2026-69730, a DNS weakness present in Windows Server 2012 onward and on Windows 10. Microsoft warns that an unauthenticated attacker could leverage this weakness simply by sending a specially crafted packet to an affected system, and that it is likely to be exploited.
Also scary is CVE-2026-69829, a critical, remote code execution flaw in the Windows Shell. This vulnerability has a CVSS base score of 9.8 (10 is the most severe), and can be exploited with low attack complexity, no privileges, and no user interaction.
Whatever else AI is or isn’t good at, it seems to be great at finding security flaws in Microsoft products…
It’s incredibly important to own physical media, because you do not know what people are going to do that work for these massive tech companies. Once they get a hold of the data and they put it into those AI [slop] machines, because that’s what they are, they can change anything. Half the stuff that people, when they Google things or whatever, that just comes out with some AI thing that’s based on something that somebody wrote on Reddit six years ago that’s probably not even true. Maybe it is, maybe it isn’t. Who actually knows whether it’s true? It’s kind of like if you listen to a record on Spotify that says remastered in 2018, remastered in 2022, remastered in 2012, that’s not the original version. What they’ve done is they’ve either taken the original version, the mastered version, and just remastered it and made it sound worse, or you don’t know what they’ve actually done to it.
Another weird blog tidbit that may only be of interest to myself: Starting October 6, 2025 and running through February 9th, 2026, the Internet Archive took multiple daily snapshots of my blog after a long period of snapshotting it on a somewhat random basis, sometimes several time a week, and sometimes only a few times a month. I would say the optimal periodicity would be once a day, but I have no idea how the process works.
This is Charlotte. While everyone’s losing their minds over delayed flights and tiny seats, this Jack Russell snagged a blue balloon at the airport and turned the terminal into her own racetrack. Pure zoomie chaos in the best way on Red Bull levels. https://t.co/v8WbxBxT33
— Puppies & Positivity (@Puppieslover) March 4, 2026
This starts out as a warning that off-brand digital devices can be doing sketchy stuff behind your back and blossoms into a expose of a wide-ranging ecosystem of worldwide digital fraud.
Security experts have been sounding the alarm for years about the risks of using generic TV boxes that promise unlimited content streaming for a one-time fee, warning that they secretly rent the user’s Internet connection out to strangers. But a groundbreaking new analysis finds these devices also routinely spoof themselves as mobile phones clicking ads on AI-generated websites as part of a sprawling operation that seeks to defraud online merchants and advertising networks.
Pedro Falé is a threat researcher with the security firm Bitsight. Falé told KrebsOnSecurity he was able to peer inside a vast and complex ad fraud network by registering an expired domain name that was used to coordinate fake ad clicks across a particularly popular brand of these streaming devices known as H96.
Falé said the domain he scooped up was previously used for telemetry, periodically collecting full hardware information and the entire list of installed apps from tens of thousands of H96 streaming sticks plugged into television sets around the globe. But upon inspecting the traffic being funneled to the domain, he discovered nearly all of the TV boxes transmitting data claimed to be mobile phone models from a variety of manufacturers, including Samsung, Vivo, Huawei, and Xiaomi.
“We noticed something was wildly wrong,” Falé said. “Multiple devices reporting to this factory Android TV Box backdoor were ‘phones.’”
The researcher found all of the devices reported having the same two apps installed, and that those apps were made by a company called Zhejiang Fengwo IoT Technology Ltd, an entity founded in 2019 in mainland China which operates an ad-publishing portfolio under the name Fengwo Group. Further investigation into the Fengwo Group revealed it has registered multiple patents that match the inner workings of these apps.
A Chinese company involved with fraud? Imagine my shock.
“Bitsight TRACE identified several Hong Kong, Singapore, and single person ‘legal’ shell identities used to collect the monetization and traced the operation back to a mainland China company known as Zhejiang Fengwo IoT Technology Co., Ltd, which operates under the Fengwo Group,” Falé wrote in a report released today about their findings.
Falé said an analysis of the apps shows they help to coordinate an ad fraud network that uses these H96 devices as a captive traffic source to click on ads at AI-generated websites operated by the Fengwo Group.
I have heard the bots signing, each to each…
Bitsight discovered the websites contain machine-generated news articles and graphics across a range of categories, including finance, health, education, gaming, music and food blogs. But they also found none of those sites displayed ads unless the device visiting the page matched the spoofed mobile profile of these H96 devices.
The domain for the Fengwo Group — fwgcloud[.]com — claims the company is “redefining the boundaries of human-AI interaction,” and that it has created more than 120,000 “AI digital humans” available to rent for everything from emotional companionship to 24/7 customer service and creative design.
Falé said the Fengwo Group’s domain shared its SSL certificate data with other domains associated with the apps found on H96 devices, specifically the phone spoofing mechanism. He noted the domain also has an internal wiki platform that directly ties the Fengwo Group to a proprietary implementation of a Google-built visual programming language called Blockly, which was originally designed to help kids learn how to write software.
According to Bitsight, the Fengwo Group’s employees use Blockly to build the sham websites, allowing low-skilled operators to drag blocks of code together in their Blockly editor — without any need to understand what the underlying code blocks do or how they work.
That’s pretty weird. “I broke into CitiBank using a program I wrote in Logo!”
“An operator can drag blocks together in their Blockly editor, to define each fraud routine, given a task type,” reads Bitsight’s report. “Once the routine is saved, it gets exported as JavaScript and uploaded to the S3 buckets. An operator doesn’t need as much understanding of the underlying technicalities, as it is all set in place for ease of use.”
Bitsight even found one of the Fengwo Group app developers mentioning exactly these advantages, noting the developer remarked that “only a small number of highly-skilled developers are needed to build the template execution-unit images,” and that “developers who create execution units from those templates have significantly lower technical requirements, greatly reducing the company’s operating costs.”
Falé said if a user’s H96 streaming stick is selected for a specific fraud task, it will be pushed the appropriate Blockly module according to the task desired, which can include silently launching a web browser, visiting websites, browsing pages, managing tabs, and clicking on ads.
To ensure the TV boxes masquerading as mobile phones can reliably click on ads displayed via the AI-generated websites, the Fengwo group “fuses three vision and reasoning systems into a single interface,” allowing the bots to correctly identify an ad on the webpage and navigate the site much like a human would, the Bitsight report observed.
It gets weirder.
Bitsight found the H96 devices were either relaying residential proxy traffic or participating in ad fraud, but never both at the same time. In fact, they concluded that when these TV boxes detect an HDMI signal from an attached television — indicating the user intends to stream video content — the box is usually functioning as a residential proxy. When the TV is off, it switches back to waiting for ad fraud jobs.
Falé said he believes the TV boxes are set up this way because its ad fraud activities are far more resource intensive and could interfere with the device’s stated purpose — streaming video content over the Internet.
Despite repeated warnings from the FBI and security industry leaders about the security and privacy risks of using these streaming devices, major e-commerce providers like Amazon, Best Buy, Newegg and others continue to sell hundreds of different models and brands that bundle unofficial versions of Google’s Android operating system and are frequently marketed (via online influencers) as a way to access a broad array of streaming services and live broadcasts without a subscription.
In addition to enlisting the user’s TV box in ad fraud networks, these off-brand streaming devices almost universally come with residential proxy software pre-installed. This software rents the user’s Internet address out to anonymous paying customers, who run the gamut from aggressive content scraping firms to ticket scalpers and outright cybercriminals.
What’s more, because these generic (and generally dirt cheap) TV boxes are all horribly insecure by default and bereft of any kind of authentication, installing one on your home or office network only invites further mischief. In January, the proxy tracking service Synthient documented how multiple botnets had rapidly enslaved millions of TV boxes using a complex interplay of security vulnerabilities in both the residential proxy software and the streaming devices themselves.
Bitsight said it tracked approximately 38,000 TV boxes globally phoning home to the expired Fengwo Group domain, and based on that number the report estimates this ad fraud network brings in revenues of close to $50,000 a day (not counting substantial revenue from the residential proxy side of the business). However, Falé emphasized that these estimates are highly conservative and based on telemetry from just one of the Fengwo Group’s core (but older) domains.
As for the Fengwo Group’s claim to have 120,000 “digital humans” at their disposal, Bitsight’s report concludes it could be just a clever marketing scheme and/or a way to avoid drawing suspicion to the company’s operations.
“Historically, when dealing with proxy services or DDoS, we sometimes see these websites undertake inconspicuous facades, so as not to advertise their DDoS capability or botnet size,” Falé wrote in the report. “This could also be the case here.”
So remember: When you buy a cheap, crappy digital device from TEMU or Amazon, you might be setting up a cheap fraud bot for Communist China.
A pilot is returned (at the cost of a few airframes), more high-ranking IRGC and Hezbollah scumbags dirtnapped, a ballistic warhead plant blows up real good, and a Soleimani offspring gets skanky.
Both F-15 pilots have now been safely rescued from Iran:
FROM PRESIDENT DONALD J. TRUMP
WE GOT HIM! My fellow Americans, over the past several hours, the United States Military pulled off one of the most daring Search and Rescue Operations in U.S. History, for one of our incredible Crew Member Officers, who also happens to be a highly respected Colonel, and who I am thrilled to let you know is now SAFE and SOUND! This brave Warrior was behind enemy lines in the treacherous mountains of Iran, being hunted down by our enemies, who were getting closer and closer by the hour, but was never truly alone because his Commander in Chief, Secretary of War, Chairman of the Joint Chiefs of Staff, and fellow Warfighters were monitoring his location 24 hours a day, and diligently planning for his rescue. At my direction, the U.S. Military sent dozens of aircraft, armed with the most lethal weapons in the World, to retrieve him. He sustained injuries, but he will be just fine. This miraculous Search and Rescue Operation comes in addition to a successful rescue of another brave Pilot, yesterday, which we did not confirm, because we did not want to jeopardize our second rescue operation. This is the first time in military memory that two U.S. Pilots have been rescued, separately, deep in Enemy Territory. WE WILL NEVER LEAVE AN AMERICAN WARFIGHTER BEHIND! The fact that we were able to pull off both of these operations, without a SINGLE American killed, or even wounded, just proves once again, that we have achieved overwhelming Air Dominance and Superiority over the Iranian skies. This is a moment that ALL Americans, Republican, Democrat, and everyone else, should be proud of and united around. We truly have the best, most professional, and lethal Military in the History of the World. GOD BLESS AMERICA, GOD BLESS OUR TROOPS, AND HAPPY EASTER TO ALL!
Evidently extracting the pilot was a considerable operation:
“Two C-130 Hercules & Little Bird Destroyed.” Evidently they got stuck in the sand and had to be destroyed by American forces after the crew were rescued. Plus reports of a running gun battle where American forces had to stomp more Iranian hostiles.
Ed Driscoll at Instapundit put up several tweets at foreigners not understanding that America cares a whole lot more about the lives of pilots than replaceable hardware.
Checking in on “Le Dying Empire” meme:
The US lost one 40 year old fighter jet over the course of 12,000 combat sorties then immediately rescued the pilot in hostile territory – while simultaneously sending astronauts to the moon. https://t.co/5XAulhMCWGpic.twitter.com/0Oti3WLAE5
You once were the feared boogie man of the Middle East. Instead, you get the complete shit kicked out of you for 5 weeks straight, your entire navy sunk, your supreme leader killed, and you FINALLY shoot down 1 plane
You once were the feared boogie man of the Middle East. Instead, you get the complete shit kicked out of you for 5 weeks straight, your entire navy sunk, your supreme leader killed, and you FINALLY shoot down 1 plane
This is finally your moment. You can parade the pilot on TV and use him as negotiating leverage
But instead, Air Force Pararescue puts boots on the ground on your home turf, we basically build a whole patrol base including a Forward Air Refueling Point, kill hundreds of your dudes, something goes wrong with one of the C-130s at the FARP on our way out, we’re not even cortisol spiked so we simply just fly in another plane and blow up the old one instead of even bothering to do any maintenance just because of how much money we have that we can simply buy a new plane
Good grief. I haven’t seen a beatdown this bad since Will Stancil got molested by Grok. This is honestly embarrassing for the IRGC at this point. That was LITERALLY your home territory where you know all the terrain and have home field advantage, we have never done real boots on the ground operations in Iran before, and you still lost.
“Iranian state-affiliated media report that Mohammad Ali Fathali-Zadeh, a brigadier general in the Islamic Revolutionary Guard Corps and commander of the Fatehin unit, was killed on Wednesday.”
“IDF Eliminates Senior Commander of Hezbollah’s 1800 Terror Unit in Beirut Strike… Israeli fighter jets “conducted a strike in Beirut and eliminated Hamza Ibrahim Rakin, Deputy Commander of Unit 1800, along with the unit’s Operations Officer.”
“Israel strikes ballistic warhead plant, ‘heart’ of Iran’s military complex in air strikes on Tehran.” It blew up real good.
Caveat: Real explosions are interspersed with AI videos of the tunnels underneath.
“Iran’s highest bridge linking Tehran to Karaj is struck in a joint US-Israeli strike.”
Tousi is reporting inter-regime strife between different elements over controlling the government.
A financially motivated data theft and extortion group is attempting to inject itself into the Iran war, unleashing a worm that spreads through poorly secured cloud services and wipes data on infected systems that use Iran’s time zone or have Farsi set as the default language.
Experts say the wiper campaign against Iran materialized this past weekend and came from a relatively new cybercrime group known as TeamPCP. In December 2025, the group began compromising corporate cloud environments using a self-propagating worm that went after exposed Docker APIs, Kubernetes clusters, Redis servers, and the React2Shell vulnerability. TeamPCP then attempted to move laterally through victim networks, siphoning authentication credentials and extorting victims over Telegram.
Also from Ed Driscoll, the niece of Qasem Soleimani living like a slutty American girl here while supporting the mullah regime:
I was considering this from the American perspective, but from the Arabic, Iranian, and Muslim perspective this is a huge propaganda coup for the American government. These photos completely discredit Iran, at a moment when Iranian soldiers are deserting and demoralized. https://t.co/oGsNeTh97opic.twitter.com/3zRcJ1eIMB
Iranian is still lobbing missiles at its neighbors. “Iranian forces struck Bahrain’s BAPCO oil refinery this morning, setting the facility’s tank farm ablaze.”
Prophecy for two days from now: “U.S. President Donald J. Trump in a post Easter Sunday directed at Iran via TruthSocial: “Tuesday will be Power Plant Day, and Bridge Day, all wrapped up in one, in Iran. There will be nothing like it!!! Open the Fuckin’ Strait, you crazy bastards, or you’ll be living in Hell – JUST WATCH! Praise be to Allah. President DONALD J. TRUMP.”
As always, these are just the stories I was able to gather I thought important enough to include. If you think I missed anything important, feel free to share it in the comments below.
Congratulations on making it to the end of a difficult but exhilarating 2024, and I hope you had a Merry Christmas! Christmas week is always slow, so this will be a smaller LinkSwarm than usual, and thank goodness for that. More Biden misdeeds, lots of Russian stuff blows up, two horrible gay pedophiles go to prison forever, and Democratic judges going out of their way to punish the victims. Let’s dig in!
President Joe Biden is transferring more student loan debt onto American taxpayers with only weeks left until he departs the Oval Office.
The Biden administration announced Friday that it is giving $4.28 billion of student debt relief to almost 55,000 more public service workers including teachers, nurses, and law enforcement officials.
“From Day One of my Administration, I promised to make sure that higher education is a ticket to the middle class, not a barrier to opportunity,” Biden said in a statement.
“Because of our actions, millions of people across the country now have the breathing room to start businesses, save for retirement, and pursue life plans they had to put on hold because of the burden of student loan debt.”
The Department of Education is forgiving the debt through the Public Service Loan Forgiveness program, a policy that permits the forgiveness of remaining student loans for public employees who have made 120 monthly payments.
Federal bureacurats are simply more equal than mere citizens…
Remember how Biden commuted and pardoned some of the worst people in the world earlier this month? Well, he found worse ones still.
President Joe Biden on Monday commuted the sentences of 37 of the 40 men on federal death row, reclassifying their sentences to prevent President-elect Donald Trump from allowing their executions when he returns to office in January.
The 37 men were all convicted of murder. Their sentences will be reclassified from execution to life in prison without the possibility of parole, according to the White House.
The men whose sentences are being reclassified include Shannon Agofsky, who murdered a bank president, dumped his body in a lake, and then killed another man in prison; Brandon Basham and Chadrick Fulks, who escaped from prison and killed two women while on a 17-day crime spree; Ricky Allen Fackrell, a white supremacist who killed a prison inmate; and Daryl Lawrence, who killed a police officer during a bank robbery.
“Make no mistake: I condemn these murderers, grieve for the victims of their despicable acts, and ache for all the families who have suffered unimaginable and irreparable loss,” Biden said in statement. “But guided by my conscience and my experience, . . . I am more convinced than ever that we must stop the use of the death penalty at the federal level.”
Biden only left three men on federal death row: Robert Bowers, the gunman who shot and killed eleven worshipers at the Pittsburgh Tree of Life synagogue in 2018; Dylann Roof, a white supremacist who killed nine people at a black church during a Bible study in 2015; and Dzhokhar Tsarnaev, the 2013 Boston Marathon bomber.
Biden’s so opposed to the death penalty he only refused to commute sentences for those criminals the public would pay attention to…
Do blue state Democratic officials think they can defy the federal government on deporting illegal aliens? A hard rain is gonna fall.
Hoover Institution senior fellow Victor Davis Hanson said Thursday that incoming border czar Tom Homan is starting with Democratic Chicago to deport illegal immigrants in order to set a precedent for other cities threatening to block his efforts.
Since President-elect Donald Trump’s nomination of Homan as border czar, the former Immigration and Customs Enforcement (ICE) acting director has warned Democratic mayors to step aside as some have threatened to refuse cooperation with ICE on mass deportations.
Snip.
Hanson argued that Homan’s focus on Democratic Chicago Mayor Brandon Johnson will set a precedent, emphasizing that the incoming border czar is listening to Democratic constituents concerned about illegal immigration in their city.
Snip.
I know the most obnoxious, the most crazy, the most nullification advocate in one of the second or third largest cities is Chicago, that crazy Mayor Johnson,’” Hanson continued. “‘So we’re going to tell him first, you try to stop the federal government and you think you’re South Carolina 1832 or you think you’re firing on Fort Sumner. You’re going to regret it because you were breaking federal law and we have a lot more federal laws that you would want us to follow in your interest than you do federal laws to break.’”
“That’s going to be interesting because what Homan is basically doing is talking over the mayor’s head to the black constituencies of Chicago and saying, don’t worry, your mayor doesn’t, he’s going to break the law, but I’m going to follow it and I’ll put him in jail for your benefit so that you don’t have to worry about Venezuelans and Colombians shooting you or taking over your social services,” Hanson added.
U.S. President-elect Donald Trump plans to continue military support for Ukraine, the Financial Times reported on Dec. 20, citing undisclosed sources.
Three officials familiar with discussions revealed that Trump intends to keep supplying US military equipment to Ukraine after his inauguration.
Trump’s foreign policy team also informed European officials that he plans to push NATO allies to raise their defense spending to 5% of their GDP. NATO member states currently follow a goal of allocating 2% of their GDP to defense spending.
A Georgia couple was sentenced to 100 years in prison without parole after adopting two boys and sexually abusing them.
William and Zachary Zulock will each spend the rest of their lives behind bars, after pleading guilty to aggravated sodomy, aggravated child molestation, incest, and sexual exploitation of children. Each were sentenced on Dec. 19.
Sanders said he first encountered some of these services while investigating Kremlin-funded disinformation efforts in Ukraine, as they are all useful in assembling large-scale, anonymous social media campaigns.
According to Sanders, all 122 of the services he tested are processing transactions through a company called Cryptomus, which says it is a cryptocurrency payments platform based in Vancouver, British Columbia. Cryptomus’ website says its parent firm — Xeltox Enterprises Ltd. (formerly certa-pay[.]com) — is registered as a money service business (MSB) with the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC).
Sanders said the payment data he gathered also shows that at least 56 cryptocurrency exchanges are currently using Cryptomus to process transactions, including financial entities with names like casher[.]su, grumbot[.]com, flymoney[.]biz, obama[.]ru and swop[.]is.
These platforms are built for Russian speakers, and they each advertise the ability to anonymously swap one form of cryptocurrency for another. They also allow the exchange of cryptocurrency for cash in accounts at some of Russia’s largest banks — nearly all of which are currently sanctioned by the United States and other western nations.
An analysis of their technology infrastructure shows that all of these exchanges use Russian email providers, and most are directly hosted in Russia or by Russia-backed ISPs with infrastructure in Europe (e.g. Selectel, Netwarm UK, Beget, Timeweb and DDoS-Guard). The analysis also showed nearly all 56 exchanges used services from Cloudflare, a global content delivery network based in San Francisco.
“Purportedly, the purpose of these platforms is for companies to accept cryptocurrency payments in exchange for goods or services,” Sanders told KrebsOnSecurity. “Unfortunately, it is next to impossible to find any goods for sale with websites using Cryptomus, and the services appear to fall into one or two different categories: Facilitating transactions with sanctioned Russian banks, and platforms providing the infrastructure and means for cyber attacks.”
“Wells Fargo Exits Net-Zero Banking Alliance After Texas Probe Into Anti-Energy Policies Attorney General Paxton has ended a review of the bank and allowed state governmental entities to do business with Wells Fargo again.”
Another day, another fake hate crime hoax. “A Tennessee college revealed that racist messages found written on campus were fabricated by a student in an apparent attempt to make Donald Trump supporters look bad. Rhodes College confirmed to Fox News Digital that a student had admitted to leaving the messages strewn about campus that were found over Thanksgiving break and were being investigated as a hate crime. Instead, it turned out to be yet another race hoax.”
Georgia woman arrested for evicting squatter from her house. And then the judge scolded her for her “privilege.” Sounds like a whole lot of people need federal equal protection lawsuits filed against them. (Hat tip: Stephen Green at Instapundit.)
I’ve long been amazed at the hyperparasitism of the hacker exploit ecosystem, where hackers penetrate systems not to steal credit card numbers, but just to steal the resources to run bot farms. And now hackers are stealing cloud resources to run AI sexbots.
Organizations that get relieved of credentials to their cloud environments can quickly find themselves part of a disturbing new trend: Cybercriminals using stolen cloud credentials to operate and resell sexualized AI-powered chat services. Researchers say these illicit chat bots, which use custom jailbreaks to bypass content filtering, often veer into darker role-playing scenarios, including child sexual exploitation and rape.
Researchers at security firm Permiso Security say attacks against generative artificial intelligence (AI) infrastructure like Bedrock from Amazon Web Services (AWS) have increased markedly over the last six months, particularly when someone in the organization accidentally exposes their cloud credentials or key online, such as in a code repository like GitHub.
You might wonder how a company could be so stupid as to include their cloud access credentials in their GitHub repository. Having worked for a long time in the cloud/SaaS space, I can tell you: It’s easier than you think. Developers probably included it so they could do rapid testing during the development cycle (and nobody wants to go through the pain of setting up another cryptokey through two-factor authentication every damn time they want to run a test), then overlooked changing it when they rolled to production. It’s the sort of thing dev should be looking for, but there are a lot of ways (personnel change, version rollback, etc.) something like that can slip through.
Investigating the abuse of AWS accounts for several organizations, Permiso found attackers had seized on stolen AWS credentials to interact with the large language models (LLMs) available on Bedrock. But they also soon discovered none of these AWS users had enabled full logging of LLM activity (by default, logs don’t include model prompts and outputs), and thus they lacked any visibility into what attackers were doing with that access.
So Permiso researchers decided to leak their own test AWS key on GitHub, while turning on logging so that they could see exactly what an attacker might ask for, and what the responses might be.
Within minutes, their bait key was scooped up and used in a service that offers AI-powered sex chats online.
Long gone are the days when boys were initiated into onanistic pursuits by the time-honored method of finding an old issue of Penthouse under a tree in the woods, but having to use AI chatbots when there’s a veritable ocean of pornography rolling around the Internet bespeaks of a lack of imagination in today’s large cohorts of lonely men.
“After reviewing the prompts and responses it became clear that the attacker was hosting an AI roleplaying service that leverages common jailbreak techniques to get the models to accept and respond with content that would normally be blocked,” Permiso researchers wrote in a report released today.
“Almost all of the roleplaying was of a sexual nature, with some of the content straying into darker topics such as child sexual abuse,” they continued. “Over the course of two days we saw over 75,000 successful model invocations, almost all of a sexual nature.”
Ian Ahl, senior vice president of threat research at Permiso, said attackers in possession of a working cloud account traditionally have used that access for run-of-the-mill financial cybercrime, such as cryptocurrency mining or spam. But over the past six months, Ahl said, Bedrock has emerged as one of the top targeted cloud services.
Stealing computer resources to run bots for cryptocurrency mining or spam is now evidentially one of those traditional criminal enterprises like running a numbers racket or selling swampland in Florida. Perhaps this strikes you with the same “get off my lawn” unease that I felt upon first reading the phrase “90s Music Nostalgia Tour.”
“Bad guy hosts a chat service, and subscribers pay them money,” Ahl said of the business model for commandeering Bedrock access to power sex chat bots. “They don’t want to pay for all the prompting that their subscribers are doing, so instead they hijack someone else’s infrastructure.”
Ahl said much of the AI-powered chat conversations initiated by the users of their honeypot AWS key were harmless roleplaying of sexual behavior.
“But a percentage of it is also geared toward very illegal stuff, like child sexual assault fantasies and rapes being played out,” Ahl said. “And these are typically things the large language models won’t be able to talk about.”
AWS’s Bedrock uses large language models from Anthropic, which incorporates a number of technical restrictions aimed at placing certain ethical guardrails on the use of their LLMs. But attackers can evade or “jailbreak” their way out of these restricted settings, usually by asking the AI to imagine itself in an elaborate hypothetical situation under which its normal restrictions might be relaxed or discarded altogether.
“A typical jailbreak will pose a very specific scenario, like you’re a writer who’s doing research for a book, and everyone involved is a consenting adult, even though they often end up chatting about nonconsensual things,” Ahl said.
In June 2024, security experts at Sysdig documented a new attack that leveraged stolen cloud credentials to target ten cloud-hosted LLMs. The attackers Sysdig wrote about gathered cloud credentials through a known security vulnerability, but the researchers also found the attackers sold LLM access to other cybercriminals while sticking the cloud account owner with an astronomical bill.
“Once initial access was obtained, they exfiltrated cloud credentials and gained access to the cloud environment, where they attempted to access local LLM models hosted by cloud providers: in this instance, a local Claude (v2/v3) LLM model from Anthropic was targeted,” Sysdig researchers wrote. “If undiscovered, this type of attack could result in over $46,000 of LLM consumption costs per day for the victim.”
Stolen credentials paid for with stolen credit cards running stolen AI access on stolen cloud platforms to run illegal sex chatbots. It’s a veritable ecology of cybercriminality…
Democrats flee, lettuce wins, a flood of extra executives, and Musk gets out the hatchet. It’s the Friday LinkSwarm!
People leaving the Democratic Party describe it as cancer:
While Democrat voters have been leaving the party for years, their reasons have become more urgent.
“When people were feeling pushed away years ago, to the point where they were starting to walk away, there was more of a casual tone about it,” former liberal Democrat Brandon Straka, founder of #WalkAway told The Epoch Times.
“People were beginning to feel the effects of leftist, communism, Marxism infiltration into our society, our culture, and our politics.”
Straka founded #WalkAway in 2018 after making his personal decision to leave the party public while inviting others to join him. Since then, thousands of exiting Democrats made social media videos explaining why they were choosing to #WalkAway, giving Straka a window into the minds of these voters.
At that time, people were just noticing changes in the party, he said. They weren’t always identifying what it meant, but they knew they didn’t like how it felt, and quietly left.
“But now, it’s akin to cancer. Cancer doesn’t stop growing and spreading just because people don’t like it. And what’s happening with the left is no different,” Straka said. “Particularly with them getting rid of Trump, installing Biden, and the Democrats taking full control of the government. This is a cancer that’s rapidly growing and spreading now. And it’s becoming not just uncomfortable, but I think intolerable, for a lot of people.”
Drugs dealers openly selling on Broadway. Thinks to mayors Bill de Blasio and Eric Adams, and the feckless actions of Soros-backed DA Alvin Bragg, Democrats have undone not only all the hard-won law-and-order gains of Rudy Giuliani’s broken windows police, but they’ve actually brought NYC back to the nadir of the crime-ridden New York of the 1970s. (Hat tip: Sarah Hoyt at Instapundit.)
Robert Francis “Beto” O’Rourke is heading to his third high-profile defeat in five years. But he and Planned Parenthood have an ace of their sleeve: registering dead voters.
A Texas firearms dealer is suing the Biden administration for weaponizing the Bureau of Alcohol, Tobacco, Firearms, and Explosives to shut down law-abiding gun retailers over paperwork errors discovered during audits.
President Joe Biden ordered the Department of Justice in June of 2021 to enforce “zero tolerance for willful violations of the law by federally licensed firearms dealers that put public safety at risk,” but after a 500 percent increase in federal firearm license revocations for retailers over the last year, it’s clear the Biden administration isn’t just going after gun sellers who intentionally violate the law.
Punishing minor slip-ups, the lawsuit argues, draws on a drastically different interpretation of the law than the definition federal courts have held based on the Gun Control Act of 1968.
The lawsuit, to which the federal government has 60 days to respond, also argues that the Biden administration’s new policy sets an unreasonably high standard that is not applied to any other industry.
That’s why Michael Cargill, owner of Central Texas Gun Works in Austin, chose to bring this case.
Those energy-hostile Democratic Party policies just keep paying dividends: “New England facing natural gas shortages, rolling blackouts this winter.”
The reality is that the normal flow of natural gas into the region is limited and has been unable to keep up with increasing demand levels over the past decade. That means that utility operators have to rely on liquid natural gas (LNG) imports to make up the difference during peak demand periods. During such times, LNG accounts for as much as one-third of the total natural gas used for heating and electricity.
But why is that? You won’t need an ace detective to figure that out. Utility companies in New York, Connecticut, and other New England states projected supply shortfalls more than a decade ago. Fortunately, New York and Pennsylvania sit on some of the richest natural gas resources in the country, found in the Marcellus shale deposits. The companies requested new, higher-volume pipelines to carry natural gas to meet the spiraling demands of New York City, particularly at the furthest end of the gas lines in Long Island. They also urged the development of local gas production to feed those lines. Similar situations were noted all across New England.
Instead of doing that, New York refused to approve new gas lines and passed a moratorium on natural gas drilling in the state. This brings us to the current situation where the same amount of natural gas is being used, but increasing amounts of it come in the form of LNG that has to be imported either from other regions of the country or from overseas. The energy crunch in Europe is eating up a lot of the available LNG, so there may not be enough for New England this winter.
A star reporter for ABC News has been missing since an April 27 FBI raid at his Arlington, Virginia apartment.
Emmy award winner James Gordon Meek – a deep-dive journalist who was also a former senior counterterrorism adviser and investigator for the House Homeland Security Committee, abruptly quit his job of 9 years and “fell off the face of the earth,” after the raid, one of his colleagues told Rolling Stone.
A recent proliferation of phony executive profiles on LinkedIn is creating something of an identity crisis for the business networking site, and for companies that rely on it to hire and screen prospective employees. The fabricated LinkedIn identities — which pair AI-generated profile photos with text lifted from legitimate accounts — are creating major headaches for corporate HR departments and for those managing invite-only LinkedIn groups.
Last week, KrebsOnSecurity examined a flood of inauthentic LinkedIn profiles all claiming Chief Information Security Officer (CISO) roles at various Fortune 500 companies, including Biogen, Chevron, ExxonMobil, and Hewlett Packard.
Since then, the response from LinkedIn users and readers has made clear that these phony profiles are showing up en masse for virtually all executive roles — but particularly for jobs and industries that are adjacent to recent global events and news trends.
Does the Federal Reserve swapping some $6 billion worth of dollars for Swiss Francs with the Swiss National Bank mean a global financial crisis is coming? Boiling down his argument: A.) The Swiss National bank has a weekly dollar auction every Wednesday. 99%+ of the time, no one shows up for them. B.) Last Wednesday, 15 parties (meaning banks) showed up for them to the tune of some $6 billion. C.) The only reason they would do that is if they don’t trust their current repo counterparties, and D.) This is what happened when Flu Manchu hit and before the Subprime Meltdown in 2008. If it’s any consolation, they first started showing up for the latter in December of 2007, so you might have nine months to buy gold, ammunition and canned goods…
“According to the latest campaign finance reports, Republican Alexandra del Moral Mealer has raised a record-setting $4.9 million dollars in support of her campaign for Harris County Judge, outraising Democratic incumbent Lina Hidalgo 4 to 1.”
Related: “Hidalgo Booed Exiting Meeting Where GOP Commissioners Continue Boycott of Tax Increase.”
Woke reporter: Are you just super excited to coach against another black coach? Tampa Bay Buccaneers coach Todd Bowles: “We don’t see color…the minute you guys stop making a big deal about it, everyone else will as well.”
There’s a new phishing scam making the rounds. I’ve received examples of this one twice myself over the last week, and since it’s a lot more sophisticated and polished than the average email phishing scam, I think it’s worth taking a look at.
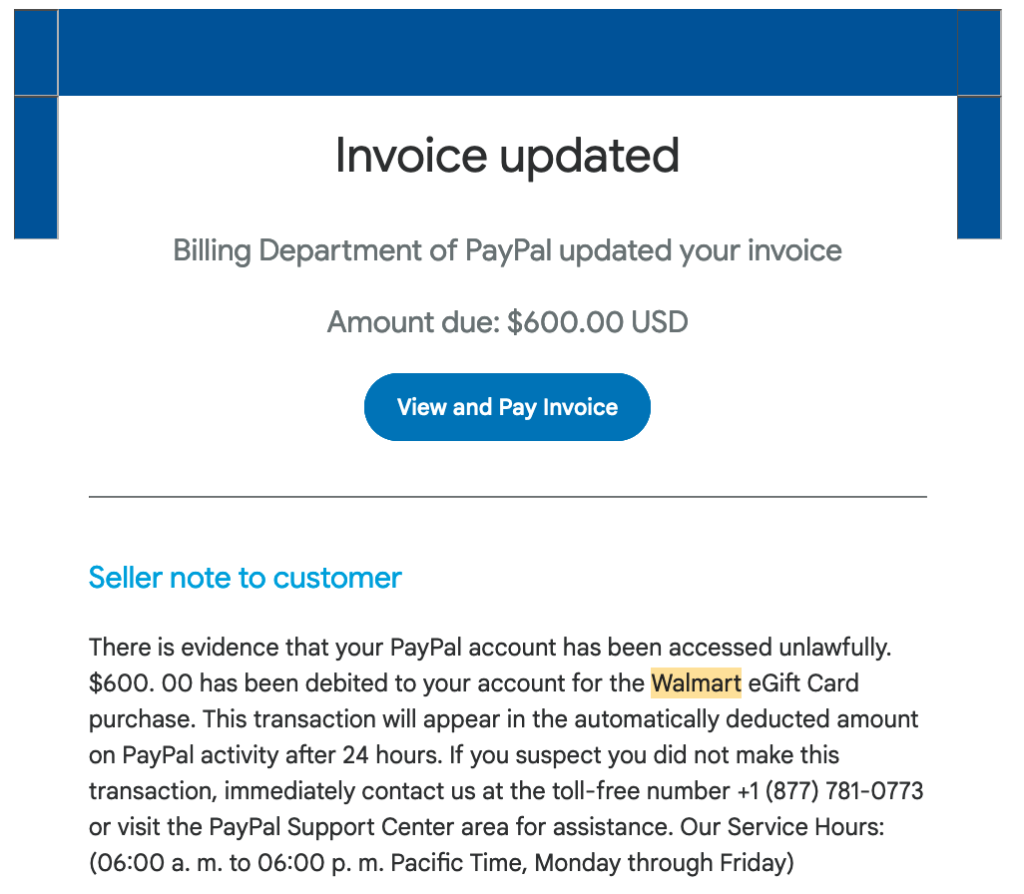
Scammers are using invoices sent through PayPal.com to trick recipients into calling a number to dispute a pending charge. The missives — which come from Paypal.com and include a link at Paypal.com that displays an invoice for the supposed transaction — state that the user’s account is about to be charged hundreds of dollars. Recipients who call the supplied toll-free number to contest the transaction are soon asked to download software that lets the scammers assume remote control over their computer.
KrebsOnSecurity recently heard from a reader who received an email from paypal.com that he immediately suspected was phony. The message’s subject read, “Billing Department of PayPal updated your invoice.”
While the phishing message attached to the invoice is somewhat awkwardly worded, there are many convincing aspects of this hybrid scam. For starters, all of the links in the email lead to paypal.com. Hovering over the “View and Pay Invoice” button shows the button indeed wants to load a link at paypal.com, and clicking that link indeed brings up an active invoice at paypal.com.
Also, the email headers in the phishing message (PDF) show that it passed all email validation checks as being sent by PayPal, and that it was sent through an Internet address assigned to PayPal.
Both the email and the invoice state that “there is evidence that your PayPal account has been accessed unlawfully.” The message continues:
“$600.00 has been debited to your account for the Walmart Gift Card purchase. This transaction will appear in the automatically deducted amount on PayPal activity after 24 hours. If you suspect you did not make this transaction, immediately contact us at the toll-free number….”
As always, look at every message from any financial institution as a potential phishing attack, so never click on links sent in email. Use your regular browser login to see if it’s a real issue, and if it’s a phishing scam, be sure to report the email in question.
Facebook, Instagram and WhatsApp are all down right now. Botched upgrade? Misconfigured router? Expired signing certificate? Who knows? I’m just going to assume its a problem with their latest SuppressAllPostsQuestioningTheHolyVaccineMarrative.yml file. But it’s a reminder of how deeply interconnected all online systems are these days, and how many different things can go wrong at different layers.
Expect a sudden burst of productivity from American companies.
Facebook—and apparently all the major services Facebook owns—are down today. We first noticed the problem at about 11:30 am Eastern time, when some Facebook links stopped working. Investigating a bit further showed major DNS failures at Facebook…
DNS—short for Domain Name System—is the service which translates human-readable hostnames (like arstechnica.com) to raw, numeric IP addresses (like 18.221.249.245). Without working DNS, your computer doesn’t know how to get to the servers that host the website you’re looking for.
The problem goes deeper than Facebook’s obvious DNS failures, though. Facebook-owned Instagram was also down, and its DNS services—which are hosted on Amazon rather than being internal to Facebook’s own network—were functional. Instagram and WhatsApp were reachable but showed HTTP 503 (no server is available for the request) failures instead, an indication that while DNS worked and the services’ load balancers were reachable, the application servers that should be feeding the load balancers were not.
A bit later, Cloudflare VP Dane Knecht reported that all BGP routes for Facebook had been pulled. (BGP—short for Border Gateway Protocol—is the system by which one network figures out the best route to a different network.)
With no BGP routes into Facebook’s network, Facebook’s own DNS servers would be unreachable—as would the missing application servers for Facebook-owned Instagram, WhatsApp, and Oculus VR.
Speculation is that Facebook engineers have locked themselves out of their own network, meaning someone with physical access to the servers will have to fix things…
Facebook and its sister properties Instagram and WhatsApp are suffering from ongoing, global outages. We don’t yet know why this happened, but the how is clear: Earlier this morning, something inside Facebook caused the company to revoke key digital records that tell computers and other Internet-enabled devices how to find these destinations online.
Doug Madory is director of internet analysis at Kentik, a San Francisco-based network monitoring company. Madory said at approximately 11:39 a.m. ET today (15:39 UTC), someone at Facebook caused an update to be made to the company’s Border Gateway Protocol (BGP) records. BGP is a mechanism by which Internet service providers of the world share information about which providers are responsible for routing Internet traffic to which specific groups of Internet addresses.
In simpler terms, sometime this morning Facebook took away the map telling the world’s computers how to find its various online properties. As a result, when one types Facebook.com into a web browser, the browser has no idea where to find Facebook.com, and so returns an error page.
In addition to stranding billions of users, the Facebook outage also has stranded its employees from communicating with one another using their internal Facebook tools. That’s because Facebook’s email and tools are all managed in house and via the same domains that are now stranded.
“Not only are Facebook’s services and apps down for the public, its internal tools and communications platforms, including Workplace, are out as well,” New York Times tech reporter Ryan Mac tweeted. “No one can do any work. Several people I’ve talked to said this is the equivalent of a ‘snow day’ at the company.”
Developing…
Edited to add 3: Seeing reports that Gmail is down for some people. It’s not down for me. I just tested and it’s working fine.
Updated to add 4: Facebook appears to be back up, but is way wonky…
Time to zig while everyone else is zagging over the Supreme Court nomination fight, and once again offer up a roundup of Communist China’s ongoing perfidy:
Chances are that by the time you get to the end of this article, there will be news of another information operation targeting Donald Trump. There’s one a day now—each trumpeting a new mortal threat to the republic or some dastardly revelation based on sources that are usually anonymous. Whatever it is, it will serve the same purpose as the hundreds of similar sallies launched over the last four years—namely, to preserve and protect the position and privileges of America’s ruling elite.
Trump stories are rarely about Trump. The same stories, or versions of them, would have targeted anyone who threatened to sever the American political, corporate, and cultural elite’s economic lifeline to the Chinese Communist Party. It is largely because Trump sought to decouple the United States from the CCP that America’s China Class, which owns the platforms on which Americans communicate, has waged a relentless campaign of information warfare against him through its social media and prestige media brands.
Consider the last two anti-Trump info ops: He gratuitously denigrated the historical suffering of African Americans, and he expressed contempt for America’s war dead. These are the sort of false allegations that political operatives are tasked to manufacture and disseminate during election season. Their purpose is to reinforce a negative impression of the opposing party among whatever cohort is being addressed, and make the target spend resources—time and money and sometimes blood—on defense. That’s politics 101, since the time of the Romans.
What’s new is that this is now journalism too. Since the internet defunded the press at the end of the 20th century and social media became the dominant player in America’s information space, journalism has abandoned the traditional standards and practices that once defined reporting. For instance, the smear holding that Trump is contemptuous of the military was supposedly based on four anonymous sources recalling exchanges from three years ago, which have been contradicted by dozens of named sources, some of whom were physically present when the comments were supposedly made—and some of whom have been public Trump opponents. In traditional journalistic terms, that’s not a news story—that’s a failed attack line.
The press that existed in America from the end of the 19th century until the turn of this one was designed to inform, influence, and sometimes inspire or inflame fellow citizens. But for people under 30, the only kind of “journalism” they’ve ever known is more like Pravda in the old Soviet Union or the kinds of party media found throughout the Third World. Journalism is an insider’s game, in which the stories are often outlandish, but rarely true; their actual news value is the hints they may offer about shadowy maneuverings that affect people’s lives but take place out of public view, like the rise or fall of a particular colonel who is pictured standing closer to or farther away from El Caudillo or Al Rais. Stories aren’t about the realities they purport to depict; the real stories are always the stories about the story.
American journalists, who now draw their paychecks directly and indirectly from the country’s largest economic interest—technopolies like Amazon, Apple, Google, and Facebook—are now turning the public sphere into a phantasmagoria of conspiracy theories and hysteria to cement the politburo’s position and privilege.
Accordingly, the debate in Washington, D.C., over which great power is feeding more disinformation into the 2020 election cycle isn’t real—it’s not Russia, as collusion impresario and Democratic Rep. Adam Schiff claims, nor, as Attorney General William Barr says, is it China, though he’s closer to the truth. The source of the purposeful disinformation pouring into the American public sphere like untreated sewage is the American elite, led by its tech oligarchs, who own the platforms on which information campaigns are staged and laundered to protect their core interests—foremost among them being cheap Chinese labor and access to Chinese markets.
Snip.
By the time the Clinton White House granted China most favored nation trade status in 2000, all of Washington knew that America was running a vast trade deficit that was destined to increase with accession to the World Trade Organization. The price for lifting tens of millions of rural Chinese peasants out of poverty through favorable trade arrangements would be tens of millions of American lives ruined, even as large American companies like Apple and Nike and bankers like JPMorgan and Goldman Sachs got richer. The elite reasoned that they had no choice: The rise of China was inevitable. Why fight it?
American political and corporate elites didn’t choose decline. They chose to get rich. By shipping America’s manufacturing base off to China, they seized a business opportunity the likes of which had never been seen before—an enormous captive labor force controlled by an authoritarian regime that guaranteed the steady production of goods at a fraction of what it would cost at home. American cultural elites (Hollywood, sports, art, etc.) who exploited the increasingly large Chinese market for their products provided cover for the China Class cohort with messaging that dovetailed with CCP propaganda.
Who were Americans to judge a great and ancient civilization like China’s for jailing dissidents and enslaving the Uighur minority? Doesn’t America have its own history of slavery and political prisoners? It’s racist to protect American jobs. Those jobs aren’t coming back and there is nothing to be done about it, as Barack Obama famously said—unless you have a magic wand …
Calling out the American elite for betraying American interests in the service of their own personal and corporate bottom lines helped Donald Trump win the presidency. But it’s not clear that he truly understood how deeply entwined Beijing’s interests were with America’s China Class—and that trying to decouple the two would lead to an attempt at a permanent coup by the new techno-elite, targeting not just him and his supporters but the foundations of the republic, from our military to the media, and from our justice system to the institution of the presidency itself.
The American elite’s financial relationship with China is the key to understanding what’s been happening in America the past four years. Any president, Democrat or Republican, who took on China would have been targeted by the China Class. Because it was Trump flying the Republican banner who sided with America’s working men and women, the Democrats resorted to alliances with powers that now threaten the stability and security of the country.
Overstated? A bit. But there are several kernels of truth in there…
Related: Major U.S. media companies that have ties to China. It’s an extensive list…
Hong Kong-based virologist Yan Li-Meng, currently in hiding at an undisclosed location, claims that the COVID-19 coronavirus came from a People’s Liberation Army lab, and not from a Wuhan wet market as Beijing has claimed.
EconoTimes reports on Yan:
Speaking on a live stream interview on Taiwan’s News Agency Lude Press, she said, “At that time, I clearly assessed that the virus came from a Chinese Communist Party military lab. The Wuhan wet market was just used as a decoy.”
“I knew that once I spoke up, I could disappear at any time, just like all the brave protesters in Hong Kong. I could disappear at any time, even my name would no longer exist,” Yan said according to a translation.
Yan has been in hiding in the U.S. after fleeing Hong Kong in April. She last made waves in July after an interview with Fox News:
Yan told Fox News in an exclusive interview that she believes the Chinese government knew about the novel coronavirus well before it claimed it did. She says her supervisors, renowned as some of the top experts in the field, also ignored research she was doing at the onset of the pandemic that she believes could have saved lives.
She adds that they likely had an obligation to tell the world, given their status as a World Health Organization reference laboratory specializing in influenza viruses and pandemics, especially as the virus began spreading in the early days of 2020.
On July 30th, Chinese state media published details of the upcoming fifth plenary session. The Party’s leaders have traditionally used the conference to lay out their next five-year plan, but this time a new detail was included—a pointed reference to “targets for 2035.” The date may give us some indication of how long Xi Jinping intends to retain his position as president. China has reached a crucial stage of its development, with superpower status at last in sight, and Xi has decided that only one man can be trusted to guide the country through the final stages of its glorious journey. That man is himself, of course. He has assumed the role of Great Helmsman, famously ordering the removal of presidential term limits in 2018 to ensure that the inferior leaders of the future don’t botch the job.
In the years since becoming president, Xi has drawn state powers to himself like no other Chinese leader since Mao. Today he oversees all aspects of economic, political, cultural, social, and military reform, and at the same time he directs all aspects of national, internet, and information security.1 This dramatic fortification of his personal power requires him to focus on the silencing of dissent—again, to a greater degree than any of his predecessors since Mao. But dissent crops up in many and varied forms, even in China, and as a result we find that the president’s power base is built on countless personal tragedies.
Xi has authorised his secret police to kidnap, “interrogate” (torture), and detain for six months anyone charged with endangering state security, which means, in reality, anyone who has expressed heretical views. Tens of thousands have disappeared as a result. Others have been caught in his anti-corruption dragnet—a convenient cover for him to get rid of dissenting voices. And more than a million people have been locked in concentration camps, most of them guilty only of belonging to the wrong ethnic group. If Xi really does stay in power until 2035 then we can expect the casualties to keep piling up for another 15 years. We owe it to these victims to tell a few of their stories, and to remember some of their names.
Xi’s Gestapo thugs will sometimes come for TV newscasters just before they are due to go on air, but in 2018 they came for an elderly professor while he was actually on the air. Six or seven policemen turned up to drag Sun Wenguang, 83, away from his live interview with Voice of America. These are cynical terror tactics. It’s one thing to read a detached news report about someone having been arrested; it’s quite another to actually hear the panic in the old man’s voice as he shouts: “What are you doing? What are you doing? It’s illegal for you to come into my home!” That interview will not quickly be forgotten by Chinese listeners to Voice of America.
“Deng Xiaoping kept everyone together by promising to make them rich,” says Nicholas Bequelin, East Asia Director of Amnesty International. “What keeps things together under Xi is fear. Fear of the system, where no matter how high you are, from one day to the next you can disappear.” 243 Party officials are reported to have killed themselves during Xi’s first few years in office, apparently terrified at the prospect of investigation by his dreaded Central Commission for Discipline Inspection. It is not difficult to understand why they might have chosen this route. Both body and will are broken in the Party’s detention centres. Each of those officials knew that after just a few months in police custody, he would no longer be the same person.
Several sad examples of Chinese individuals broken by torture snipped.
Xi Jinping has more in common with an emperor of the ancient world than the chairman of a revolutionary vanguard party. Despite this, somewhat paradoxically, he has resurrected the language of Mao’s era. In the words of John Garnaut, one-time advisor to the Australian government, “Xi’s language of ‘party purity’; ‘criticism and self-criticism’; ‘the mass line’; his obsession with ‘unity’; his attacks on elements of ‘hostile Western liberalism,’ ‘constitutionalism,’ and other variants of ideological ‘subversion’—this is all Marxism-Leninism as interpreted by Stalin as interpreted by Mao.”
The Communist Party of the 21st century is a classic Chinese dynasty rather than the temporary guardian of a workers’ revolution. Its leaders are concerned with the Party itself, not with communism. But Xi is using elements of Marxism-Leninism as the glue to hold society together—like a religion, perhaps, or like Confucianism in earlier dynasties. “Our red nation will never change colour,” he tells the people. And with the return of the old phrases comes the return of the old practices. Xi knows that Western ideas are forever infecting the minds of his subjects; always perverting the purity of students, of lawyers, of government officials. Like Stalin and Mao, he knows that regular purges are necessary in order to preserve the spiritual health of the people.
Xi’s main legacy, however, is surely the Xinjiang nightmare. Over the past few years a million or more Uyghur Muslims (and smaller numbers of Kazakhs and Kyrgyz) have been shut in concentration camps scattered about the western province. This mass incarceration is a response to terrorist attacks carried out by Uyghur separatists in Kunming and Ürümqi in 2014—attacks that came at the end of decades of tension between Uyghurs and Han Chinese, the country’s dominant ethnicity.
The camps are designed to stamp out extremist thinking. Unfortunately, as with so many of Xi’s policies, there is no concern for collateral damage. Party leaders have been given instructions to round up anyone acting suspiciously, but this definition of “suspicious” appears to have been provided by a paranoid schizophrenic. Uyghurs have been interned for growing a beard; making plans to travel abroad; praying too much (or, on other occasions, not praying enough); setting clocks to two hours after Beijing time; even simply having been born in the 1990s. The wrong skin colour is itself cause for suspicion.
From the outset, Xi told his officials to show no mercy. They took him at his word, and now the personal tragedies are mounting.
— Color Revolutionary Poso (@JackPosobiec) August 3, 2020
China's planned route to the Arabian Sea is key for their Westward expansion – and strategically located next to the India-China border, not to mention their largest oil supplier Iran, and of course, Afghanistan.
The conventional wisdom has long been that, if there is to be a major war involving China and the U.S., it will be the result of either of a rising China initiating war to displace the failing U.S. hegemon, or a declining U.S. initiating a war to stymie a rising China. But this ignores the possibility that systemic or hegemonic war between China and the U.S. may not have anything to do with a rising power. It ignores the possibility that such a war might be initiated by what I will call a faltering contender, a once-rising power whose ascent is running out of steam and whose leaders believe that it must decisively reshape the global order now while it still can.
The logic linking a faltering bid for hegemony to systemic war is simple enough. Faced with the prospect that it is losing the demographic or developmental race with other potential challengers, or merely with non-hegemonic rivals, a faltering contender will sometimes launch what might be thought of as a war of desperation. In this kind of war, a faltering contender will initiate hostilities because, having realized that it has reached the peak of its relative power, it decides it must initiate war now, even under unfavorable circumstances, because if it doesn’t, it will not only fail to achieve predominance but will face the prospect of catastrophic defeat in the near future. Such wars are not caused by states leaping through open windows of opportunity created by the military advantage they enjoy over their potential rivals. Instead, they are caused by stalled rising powers, at a current or imminent military disadvantage, attacking despite this disadvantage because it is the least bad of several very bad options open to them.
Analogies to Germany in World War I and Japan in World War II snipped.
China’s explosive economic growth since the beginning of reform in 1979 is a unique success story, as is the concomitant growth of its military power and global influence. Few could have predicted that within one generation of Richard Nixon’s visit to Beijing in 1972, China would have risen to undisputed number two in the global pecking order. China now has the world’s second-largest economy, a world-class military with growing force projection capabilities, a worldwide network of ‘silk roads’ making it a central node in the global economy, and a diplomatic profile that makes it, if not an ‘indispensable nation,’ then something pretty close. And yet, at precisely the moment when its tide has reached heights not seen for centuries, the Chinese leadership has reason to believe that China’s star may not be in the ascendant much longer. President Xi’s failed One-Belt initiative, botched COVID-related ‘medical soft power’ play, abrogation of the ‘one-country, two-systems’ modus vivendi with Hong Kong, inconclusive border clashes with India, failure to sustain China’s economic momentum, policy-induced demographic time-bomb, and a growing sentiment that China is becoming less powerful and therefore less relevant player on the world stage suggest that China is no longer a rising power, but a faltering one. Viewed through this lens, the picture of the future that comes into focus is one of counterbalancing, containment, economic ‘decoupling,’ social turmoil, ethnic unrest, and general entropy culminating in collapse. Unless a forward-thinking Chinese leader might conclude, decisive steps are taken now to put things aright. And what might those steps be? Well, if history is any guide, they might include launching a war of desperation in the hope of securing the best geopolitical settlement possible before China is weakened to the point where it is simply condemned to another ‘hundred years of humiliation.’ What that war might look like – how it might erupt, whom it might involve, what course it might take – cannot be forecast with any certainty. But then neither could the war started by Germany in 1914 nor that by Japan in 1941. The point is that in those two earlier cases, the only rational course of action for the faltering challenger was the strategic Hail Mary pass. The question is, will a China whose rise is similarly stalling throw a comparably desperate strategic pass the early in the 21st century?
The U.S. Justice Department this week indicted seven Chinese nationals for a decade-long hacking spree that targeted more than 100 high-tech and online gaming companies. The government alleges the men used malware-laced phishing emails and “supply chain” attacks to steal data from companies and their customers. One of the alleged hackers was first profiled here in 2012 as the owner of a Chinese antivirus firm.
Charging documents say the seven men are part of a hacking group known variously as “APT41,” “Barium,” “Winnti,” “Wicked Panda,” and “Wicked Spider.” Once inside of a target organization, the hackers stole source code, software code signing certificates, customer account data and other information they could use or resell.
APT41’s activities span from the mid-2000s to the present day. Earlier this year, for example, the group was tied to a particularly aggressive malware campaign that exploited recent vulnerabilities in widely-used networking products, including flaws in Cisco and D-Link routers, as well as Citrix and Pulse VPN appliances. Security firm FireEye dubbed that hacking blitz “one of the broadest campaigns by a Chinese cyber espionage actor we have observed in recent years.”
Snip.
One of the men indicted as part of APT41 — now 35-year-old Tan DaiLin — was the subject of a 2012 KrebsOnSecurity story that sought to shed light on a Chinese antivirus product marketed as Anvisoft. At the time, the product had been “whitelisted” or marked as safe by competing, more established antivirus vendors, although the company seemed unresponsive to user complaints and to questions about its leadership and origins.
Those charged also include Zhang Haoran, Jiang Lizhi, Qian Chuan and Fu Qiang.
The Trump administration plans to soon scrap a 2013 agreement between U.S. and Chinese auditing authorities, a senior State Department official said, a move that could foreshadow a broader crackdown on U.S.-listed Chinese firms under fire for sidestepping American disclosure rules.
The deal, which set up a process for a U.S. auditing watchdog to seek documents in enforcement cases against Chinese auditors, was initially welcomed as a breakthrough in U.S. efforts to gain access to closely guarded Chinese financial information and bestowed a mark of legitimacy on Chinese regulators.
But the watchdog, known as the Public Company Accounting Oversight Board (PCAOB), has long complained of China’s failure to grant requests, meaning scant insight into audits of Chinese firms that trade on U.S. exchanges.
The lack of transparency has prompted administration officials to lay the groundwork to exit the deal soon, according to Keith Krach, undersecretary for economic growth, energy and the environment, in a sign the PCAOB will give up on efforts to secure information from the Chinese.
His doctorate research was about Chinese foreign policy and he was about to discover firsthand how the rising superpower seeks to attain influence.
After his presentation, Jun Wei, also known as Dickson, was, according to US court documents, approached by several people who said they worked for Chinese think tanks. They said they wanted to pay him to provide “political reports and information”. They would later specify exactly what they wanted: “scuttlebutt” – rumours and insider knowledge.
He soon realised they were Chinese intelligence agents but remained in contact with them, a sworn statement says. He was first asked to focus on countries in South East Asia but later, their interest turned to the US government.
That was how Dickson Yeo set off on a path to becoming a Chinese agent – one who would end up using the professional networking website LinkedIn, a fake consulting company and cover as a curious academic to lure in American targets.
Five years later, on Friday, amid deep tensions between the US and China and a determined crackdown from Washington on Beijing’s spies, Yeo pleaded guilty in a US court to being an “illegal agent of a foreign power”. The 39-year-old faces up to 10 years in prison.
Snip.
In 2017, Germany’s intelligence agency said Chinese agents had used LinkedIn to target at least 10,000 Germans. LinkedIn has not responded to a request for comment for this story but has previously said it takes a range of measures to stop nefarious activity.
Some of the targets that Yeo found by trawling through LinkedIn were commissioned to write reports for his “consultancy”, which had the same name as an already prominent firm. These were then sent to his Chinese contacts.
One of the individuals he contacted worked on the US Air Force’s F-35 fighter jet programme and admitted he had money problems. Another was a US army officer assigned to the Pentagon, who was paid at least $2,000 (£1,500) to write a report on how the withdrawal of US forces from Afghanistan would impact China.
In finding such contacts, Yeo, who was based in Washington DC for part of 2019, was aided by an invisible ally – the LinkedIn algorithm. Each time Yeo looked at someone’s profile it would suggest a new slate of contacts with similar experience that he might be interested in. Yeo described it as “relentless”.
According to the court documents, his handlers advised him to ask targets if they “were dissatisfied with work” or “were having financial troubles”.
When globalism’s obituary is finally written, and the mourners file past in their crisp suits and pantsuits, the cause of death will almost certainly read, the People’s Republic of China.
China is the most obvious offender. Even before the Wuhan virus cut off countries from each other, the communist oligarchy had abused the world economy with massive digital theft, even more massive counterfeiting, product dumping and every possible form of economic warfare.
That’s why any halfway serious adult on the other side supports Trump’s fight against China.
Last year, even George Soros, the uber-globalist, called Trump’s trade war with China his greatest achievement. This year, during the coronavirus crisis, Soros came out against working with the People’s Republic of China against the virus.
This certainly doesn’t buttress my theory that both Soros and China are backing antifa/#BlackLivesMatter, but it doesn’t entirely invalidate either.
China threatens to retaliate to restrict drug exports to America in retaliation for America restricting semiconductor exports. I keep saying that semiconductor equipment exports are a lot more critical and less replaceable. (Hat tip: Stephen Green.)
Dozens of universities, including Columbia and Stanford, are hosting the Chinese government-funded Confucius Institute despite increasing scrutiny from the federal government.
Many elite universities with Confucius Institute programs appear to be unfazed by the Trump administration’s decision last week to designate the D.C-based headquarters of the program as a “foreign mission”—a label the U.S. government applies to entities it finds to be directly controlled by a foreign power. Despite the announcement, nearly 50 colleges and universities will continue their partnership with Confucius Institute programs, which comes with up to $1 million in Chinese government funding.
The cushy partnership between American universities and the Chinese regime has restricted academic freedom on campus, frequently forcing administrators and faculty members to self-censor to avoid Beijing’s wrath. While many universities rely on the organization to support Mandarin language classes and Chinese culture lessons, the program also bars its staff from discussing topics considered taboo by the Chinese Communist Party, such as the Xinjiang concentration camps or the Hong Kong protests.
Former deputy mayor of Jixi city in northeastern Heilongjiang Province flees to the U.S., “reveals the tight control of speech and information in China, the regime’s cover-up of COVID-19 cases, [and] Communist Party officials secretly taking medicine to prevent virus infection.” (Hat tip: Director Blue.)
Ren Zhiqiang, former chairman of a state-owned real estate group who “openly criticized Beijing’s handling of the coronavirus pandemic was sentenced to 18 years in prison on corruption charges Tuesday, a court announced.”
Many who view the rise of China, and especially its growing technological competence, with a mixture of fear and awe should ask themselves why if emphasizing critical race theory and gender studies has not been a mistake.
Greetings, and welcome to another Friday LinkSwarm! Cleanup from Harvey and Irma continues apace, and there was another London jihad terror attack.
Bomb attack on a London tube train injuries 20, but no reported deaths. “Officers believe that the blast on the train at Parsons Green, southwest London, was caused by an improvised explosive device and hundreds of detectives are now investigating with the assistance of MI5.” More west than southwest, I would say, since it’s north of the Themes and south of Earl’s Court.
Houston City Councilman Dave Martin, who represents hard-hit Kingwood, had a message for the public about the American Red Cross.
“I beg you not to send them a penny,” he said at Wednesday’s council meeting. “They are the most inept unorganized organization I’ve ever experienced.”
In part of a broader rant that also roped in a perceived lack of assistance from his native New Orleans (“Send me your darn trucks, Mitch,” he said, a plea for the Big Easy’s mayor, Mitch Landrieu, to send waste trucks westward to haul off storm debris), Martin said local folks opened shelters and gathered water and supplies to help his northeastern suburb’s evacuees.
“Don’t waste your money,” said Martin. “Give it to another cause.”
How many times must a gay Democratic mayor be accused of child sexual abuse before resigning? Judging by Seattle Mayor Ed Murray, the answer is evidently “five.” Edited to add: Forgot to mention (as Dwight does in the comments below) that Murray was a member of Illegal Mayors Against Gun Owners.
Speaking of prominent Democratic office holders who are sex offenders, Anthony Weiner is arguing he doesn’t deserve to go to prison because it’s not his fault that those darn sexy 15-year-olds keep attracting his attention and taking advantage of his sickness. See Anthony, the thing is, when normal men receive a message like “High! I’m nubile jailbait!”, we ignore it because we’re: A.) Not perverts, and B.) Not complete morons. But only the dimmest, stupidest, sickest pervert would fall for that crap when he lives under a media microscope and after it’s already ruined his life.
The Awan family Democratic House member data breach gets murkier:
On April 6, at midnight, in a small room once used as a phone booth on the second floor of the Rayburn House Office Building, a Capitol Hill Police Officer doing his security rounds discovered evidence that will possibly reveal one of the the biggest security breaches involving House Democrats by the Awan family, a group of entrusted IT staffers, according to court records, police reports and news reports.
In the small room, the U.S. Capitol Police found a laptop computer registered to Rep. Debbie Wasserman-Schultz, a Florida Democrat and former DNC chairwoman. Wasserman-Schultz had been fighting authorities for months to return the laptop, that she once claimed was not hers.
What’s more concerning, say senior House officials who spoke to Circa, is that Imran Awan was also allegedly transferring files – including documents and emails – of House Democrats to a secret server connected to the less secure House Democratic Caucus. The organization was then chaired by Rep. Xavier Becerra, who left Congress in January after being sworn in as the Attorney General of California.
The Daily Caller’s Luke Rosiak was the first to break the story and last week Rosiak reported Wasserman Schultz’s IT staffer, now indicted Awan, is believed to have planted her laptop in the Rayburn office room, along with his Pakistani ID card, copies of his driver’s license and his congressional ID badge. Awan also left behind letters to the U.S. attorney.
Awan apparently wanted the evidence discovered, according to a Capitol Hill police report on the matter.
Officials are now asking the question of why the computer was left but the answers remain elusive.
“There is no reason to accommodate all the members data on one server and one that was apparently hidden,” said the Senior House official. “Why didn’t Xavier Becerra know this because it happened on his watch? Each member had their own server to protect against this and Awan intentionally tried to hide what he had done from investigators.”
Becerra’s office did not return phone calls for comment.
The House official told Circa that Awan was also allegedly uploading “terabits of information to dropbox so he was possibly able to access the information even after he was banned from the network.” The official said there is a need for a full congressional investigation on the matter.
“I think this may lead to information as to who really accessed the DNC server – everybody talks about Russia – but look at the access (Awan) had and potentially those emails could have been sold,” the House official added.
“The U.S. House of Representatives passed a bill Thursday that will provide $1.2 trillion to fund the government past Sept. 30, and will allocate $1.6 billion towards President Donald Trump’s border wall.” This is why I don’t freak out over all the reports of President Trump’s reported amnesty deal with Democrats. It’s not that I trust Trump, it’s that I have no interest in watching the magician make flourishes with his left hand. If such an amnesty actually approaches the voting stage, then I’ll worry. (Hat tip: Director Blue.)
Still, President Trump would do well to heed Kurt Schlicter’s advice and not let Chuck Schumer play him for a fool. “What we saw isn’t the art of the deal. This is the art of being suckered.”
Democrats are intellectually lazy. Decades of demonizing conservatives failed to win the last election. Name-calling won’t win votes. Racist, sexist, even Nazi, no longer have any meaning thanks to overuse.
If Democrats want to win again, then they will have to sell their ideas, not their skin color, their sex, or any other superficiality.
It should be apparent, but evidently is not to antifa members and leaders, that the United States, despite Donald Trump being president, is not in a comparable situation to that of Weimar Germany on the eve of Hitler’s ascension to power…Leftist violence in the 1930s in Germany led many to support the Nazis in the hope they would put an end to the continuing street brawls and violence. Today, the antifa left may even help to get Donald Trump reelected in 2020.
In a poll of possible Democratic candidates for 2020, Bernie Sanders has a commanding lead over— [At this point a lynch mob broke into the writer’s house to wreck terrible vengeance upon him for mentioning the 2020 presidential election more than three years out.]
Camille Paglia says that transgender activists are committing child abuse by advocating “sex change” surgery for children.
In sex-reassignment surgery, even today, with all of its advances, cannot, in fact, change anyone’s sex. You can define yourself as a trans man or a trans woman or one of these new gradations along the scale, but ultimately every single cell in the human body, the DNA in that cell remains coded for your biological birth.
Russian company develops anti-riot truck that’s like a moving battlement. Looks like it would be adept at crushing pro-democracy protestors and Antifa equally.